Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How we replaced our host vulnerability scanner with the Datadog Agent

A year ago, Datadog’s cloud environment had grown to support tens of thousands of users across the globe. As our host fleet expanded alongside that user growth, we saw that our original system for vulnerability scanning was becoming less effective at reaching and assessing every host.
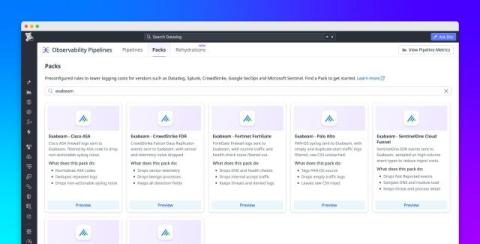
Process and route critical security logs to Exabeam with Observability Pipelines

Enterprise security teams use Exabeam as a security information and event management (SIEM) platform with user and entity behavior analytics (UEBA) to detect insider threats, lateral movement, privilege escalation, credential compromise, and data exfiltration.

The first 72 hours of a ransomware attack: Why restored isn't recovered

You start the day with reports that your employees cannot access critical systems. A ransom note soon explains why: attackers have encrypted them and demand $2 million in bitcoin for a decryption key. Your team contains the attack and confirms that the backups are safe, yet this is only the beginning. Restoring your servers can take weeks, but recovering the business can take much longer.

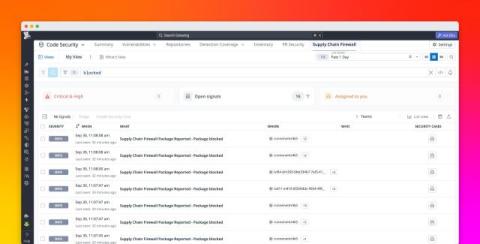
Block malicious packages across your organization with Supply Chain Firewall and Datadog Code Security

Campaigns such as Shai-Hulud 2.0 have demonstrated how quickly package malware can propagate through npm and then harvest credentials. Traditional dependency scanning can identify known risks in code once a package is added to the code, but security teams also need a check before installation.