Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

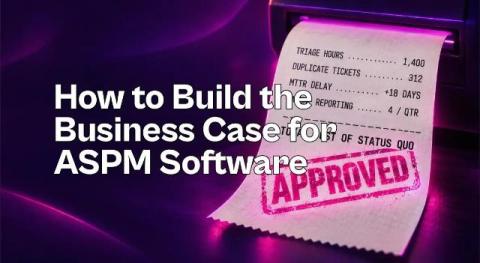
How to Build the Business Case for ASPM Software

Start with what the current backlog already costs: analyst hours spent on triage, developer time lost to duplicate tickets, slow MTTR, and manual reporting. Then tie each benefit of ASPM software to one of those costs, such as fewer tickets per fix or faster remediation. Compare pricing models on your real numbers, including integration upkeep, and propose a measurable pilot on five to ten high-value applications. Most AppSec teams don’t need to be sold on ASPM software.
Critical Bookly IDOR Leads to Booking Disclosure and Deletion (CVE-2026-93399)

During independent security research conducted as part of the Wordfence Bug Bounty Program, we identified an unauthenticated Insecure Direct Object Reference (IDOR) vulnerability in Bookly, a WordPress appointment booking plugin used to manage online scheduling, services, staff availability and customer appointments.

Risk Acceptance Has a Shelf Life: Notes from the Aviation ISAC Cybersecurity Summit

The first Aviation ISAC summit, a little over a decade ago, was about forty people in a room in Miami, hosted by the Health ISAC. This year’s conference in Vancouver hosted more than five hundred: airlines, airports, OEMs, suppliers, and government, all in one place for three days. Many in the audience were new to the conference. One of the opening speakers asked first-timers to raise their hands, and a lot of hands went up around the room.
Featured Post

What happens when a patch can't wait until next Tuesday?

Most organisations patch on a schedule. For the majority of vulnerabilities, that makes sense. Updates need testing, maintenance windows need planning and nobody wants to cause an outage while trying to fix a security problem. But what happens when something can't wait? That's the bit I think organisations need to be looking at more closely, particularly as AI starts to change how quickly vulnerabilities can be found and analysed.

Critical Security Risks in vSphere Active Directory Integration

Microsoft Active Directory is widely used for authentication, and many software solutions can integrate with it to rely on a single authentication system. VMware vSphere components, including vCenter Server and ESXi hosts, also support Active Directory integration, which simplifies account and access management. However, this convenience introduces specific security risks that administrators need to understand and mitigate.

Autonomous Attacks Are Already Here. The Defense Has to Match Their Speed.

Last week, Snyk CTO Manoj Nair sat down with Alon Krifcher, Head of Applied AI from Anthropic, for a live discussion on the coming wave of autonomous attacks. Manoj kept landing on one thing: the AI Hurricane has already arrived, and what's left is deciding whether your defense runs at the same speed as the threat.

Frontier models found the vulnerabilities. Only the attacker found the chains.

Attackers don't read your repository; they hit your URL, and chain together whatever they find. In an era where offensive AI runs against live applications at machine speed, your security tooling needs to go beyond finding vulnerabilities to prove exploitability, including whether they can be combined into a breach.

Emerging Threat: (CVE-2026-21589) Atlassian Data Center Arbitrary File Access via Path Traversal

CVE-2026-21589 is an arbitrary file access flaw affecting most of Atlassian’s self-hosted Data Center product line. CISA classifies it as CWE-552, files or directories accessible to external parties. An unauthenticated remote attacker can read specific files inside the web application root directory. The vulnerability carries a CVSS v4.0 base score of 9.3 (Critical). Attack vector is network, attack complexity is low, and neither privileges nor user interaction are required.

How we replaced our host vulnerability scanner with the Datadog Agent

A year ago, Datadog’s cloud environment had grown to support tens of thousands of users across the globe. As our host fleet expanded alongside that user growth, we saw that our original system for vulnerability scanning was becoming less effective at reaching and assessing every host.

Lost in Translation: A Native Heap Overflow in Unmaintained Jansi (CVE-2026-8484)

Jansi is the small Java package that makes colored console output work everywhere, including the Windows terminals that never understood ANSI escape codes. You may not have heard of it, but if you build Java, you almost certainly have it on disk: the Apache Maven 3.9.16 distribution puts jansi-2.4.3.jar in its lib/ directory, and Maven's pom.xml declares it as a dependency.