Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Scaling cyber protection for US critical infrastructure: How Elastic supports the Community Cyber Resilience Foundation

Over recent years, US critical infrastructure has become a primary target for coordinated cyber attacks. Small water, gas, and electric utilities have faced serious risk from cyber attacks while dealing with limited budgets, staff, and forensic expertise, leaving them further exposed. Advancements in AI have made the cyber threat landscape even more challenging. AI has become an enabler of cyber attacks, rather than a solitary perpetrator.
SIEM or XDR? Yes

Same logs, two places, overlapping outcomes. It's time to rethink the SIEM vs. XDR question. In my last blog, I asked where XDR fits into the SIEM-less conversation. To answer that, start with the endpoint. If every threat could be stopped there, there would be less need for detection and response products such as endpoint detection and response (EDR). But attackers got better at evading even the most robust endpoint security, for example by abusing dual-use tools in living-off-the-land (LOTL) attacks.

AI in the SOC: Where security teams stand

With 96% of security teams now using AI, the question is no longer whether AI delivers real value to the SOC, but one of efficiency and reliability. The recent AI Adoption in the SOC report, conducted by Dimensional Research and sponsored by Elastic, surveyed more than 400 cybersecurity professionals responsible for security operations at companies with more than 500 employees.

Build an Intelligence Advantage with Falcon Next-Gen SIEM

Every organization has a different threat profile. Industry, geography, infrastructure, business operations, and the broader technology ecosystem all influence which adversaries and threats matter most. The challenge is putting threat intelligence to work at scale to identify the greatest threats to each business. The intelligence that security teams rely on is as varied as the threats they face.

Elastic AlertZero: Who controls AI agents in the SOC?

With Elastic AlertZero, security teams can configure agent autonomy, audit agent activity, and choose the AI models that fit their environments without being locked into a single model provider. Mike Nichols, GM of Security at Elastic, explains how AlertZero addresses three priorities for bringing agentic AI into security operations: transparency, control, and model flexibility.

Every AI Agent Creates Security Debt. Most Organizations Aren't Tracking It.

Technical debt accumulates when organizations prioritize immediate speed and defer the architectural work that keeps systems dependable. Most engineering leaders know how that story ends. The shortcuts that made the first release possible eventually slow down every release after it. The agentic enterprise is creating a security equivalent.

Is "SIEM-less" really what it sounds like?

SIEM-less security may sound like an escape from traditional SIEM complexity and costs, but the underlying capabilities still have to exist somewhere. A SIEM is a multipurpose tool. It brings together cyber and physical security use cases; drives threat detection, investigation, and response (TDIR); serves as a system of record for governance, regulatory, and compliance needs; and supports observability use cases tied to resilience and service degradation. The list goes on.

How to investigate PHP2Shell-related activity with Sumo Logic

PHP2Shell is a pair of critical flaws in the PHP interpreter itself, each with a CVSS v4.0 score of 9.2. Both let an unauthenticated attacker run code on a web server with a single crafted web request, or a pair of them, before any application code runs. Because the bug lives in PHP, not in WordPress, Drupal or Magento, every reachable PHP endpoint on an affected server is exposed, including login pages, static forms, and health checks. Every PHP release from the last decade is affected (back to 5.4).

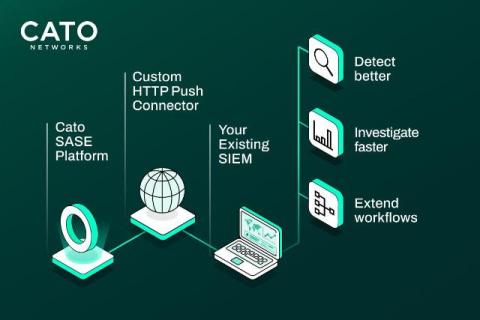
Make Your SIEM Smarter with Cato

Effective security operations require more than isolated alerts. Analysts need context from across the environment to understand what happened, assess its significance, and decide what to do next. That is why accessing insights and telemetry from across your networking and security stack is critical to teams using a SIEM tool.