Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code

Insignary Launches Clarity AIR: Closing the Blind Spot Between What Your Developers Declare and What's Actually in Your Code. New snippet-level scanning shows security and compliance leaders which open-source code and which AI-written code never made it into a manifest.
Mend.io upgrades 184 open source organizations to the Renovate Community (OSS) plan

Mend.io has proactively upgraded 184 open source organizations and GitHub users to the Mend Renovate Community (OSS) plan, with no request required. The upgrade covers about 3,000 repositories with roughly 4 million combined GitHub stars. Maintainers get higher resource limits, more concurrency, and access to Merge Confidence.

Open-Source Intelligence Tools for Security Teams

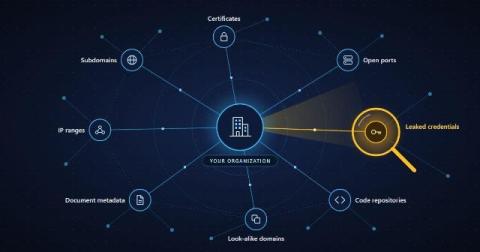
Attackers rarely start with an exploit. They start with a search: which subdomains a company runs, which staff email addresses sit in breach dumps, which forgotten server still answers on the internet. MITRE ATT&CK treats this stage as a tactic of its own, Reconnaissance, and most of it runs on public data.

Why Open Source Is the Easiest Target for Supply Chain Attacks

Attackers targeting open source dependencies already have all the code they need. Curtis Koenig, Head of Application Security at Gen, explains the fundamental asymmetry and why building quality fixes at speed is the real challenge for defenders. "An attacker can produce very fast, very ugly code that propagates through as an attack. When we're trying to fix something, the challenge we have is we're always trying to build for quality.".

Open Source Security Tools: A 2026 Guide

A mid-sized SOC can have endpoint telemetry in one platform, cloud logs in another, vulnerability findings in a third, and identity alerts somewhere else entirely. Analysts switch consoles, normalize the same event repeatedly, and still miss the incident that required context from several systems. The problem usually isn't a lack of detection technology. It's the absence of a shared data model, disciplined correlation, and evidence that security and compliance teams can use together.

10 Best Kubernetes Security Tools in 2026 [Open-Source]

Somewhere right now, someone is spinning up a fresh Kubernetes cluster, feeling pretty good with a basic firewall, skimmed a hardening guide, and maybe even applied a few CIS benchmarks. What could possibly go wrong? Roughly 18 minutes. That’s the average time before a newly exposed Kubernetes cluster receives its first malicious probe or attack attempt. So there’s zero room for error when it comes to securing Kubernetes.

Best Open-Source Container Security Tools in 2026

Have you ever tried to answer “Is this container safe to run?” If yes, then you know how tricky that question is. Securing containers is one of the toughest jobs in security, and hunting vulnerabilities across an estate of them gives security folks the same vibe as hunting in the fifth domain. Container vulnerabilities can live almost anywhere, from the image layers down to the kernel, and every week, a new base image, a new dependency, or a new manifest change opens a fresh gap.

Open-source AI Needs Security: Why Cyberhaven Is Joining the Open Secure AI Alliance

Today, Cyberhaven is joining the Open Secure AI Alliance to help advance a future in which enterprises can adopt open-source AI without compromising security, compliance, or control over their data. Cyberhaven is betting on a world where companies are free to choose from many models, agent frameworks, and open harnesses, as well as run them on infrastructure they control. That choice matters. Enterprises will not standardize on a single model or AI platform.

New Phishing Kits Use Open-Source Tools to Bypass MFA

Researchers at Lexfo are tracking three sophisticated phishing kits that were built using open-source components, primarily based on the publicly available adversary-in-the-middle (AiTM) attack framework “Evilginx.” The phishing kits are designed to proxy “live Microsoft 365 authentication sessions to capture session cookies and OAuth tokens in real time, bypassing MFA entirely.” The kits also use AI to generate personalized phishing lures with a variety of different delivery metho

How to Protect Your Repositories from Open-Source Supply Chain Attacks

The open-source trust model is broken. Not strained, not under review—broken. For years, your team has pulled third-party code into your repositories on the reasonable assumption that a widely used dependency is safe. Popularity looked like a proof. Millions of downloads looked like a security review. TeamPCP has proven otherwise.