

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Hunting Our Own Vulnerabilities First: Tanium's Frontier AI Security Commitment

Tanium’s customers span critical infrastructure sectors, including some of the largest banks, hospital systems, and government agencies in the world. They trust our agent on their most sensitive endpoints, which means that the software we ship must meet the high standards they set for themselves. That’s why we hunt our own vulnerabilities before anyone else can.

Tanium Scan Engine 7.0, "Better, Faster, Stronger": Tanium Tech Talks #170

Vulnerability and compliance scans just got faster with Tanium's new scan engine. Today we're digging into Tanium Scan Engine 7.0, a rebuild of Comply scanning that moves enumeration onto Tanium Index instead of scanning live every time. The result: faster scans, lower resource usage, and one less dependency to worry about (goodbye, JRE!!).

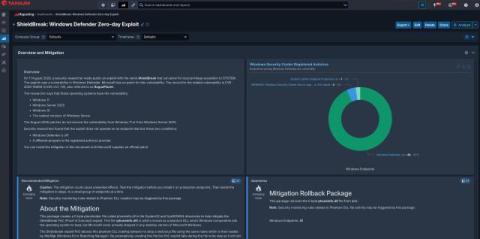
Hunt or be Hunted: ShieldBreak Zero-Day

On August 11, 2026, a security researcher publicly released a proof-of-concept called ShieldBreak, a full bypass of Microsoft’s own July patch (RoguePlanet) for a Windows Defender privilege-escalation flaw, with a reported 100% success rate against Windows 11 25H2 and Windows Server 2025. No vendor fix existed for the bypass. The only real defense was whoever moved first.

Autonomous Patch Management: Continuous, Closed-Loop Remediation

A critical vulnerability is discovered. Minutes later, it's patched — approved, scheduled, and deployed, with no one bouncing between systems to make it happen. In this video, Steven Payne shows how Tanium and ServiceNow close the gap between finding a problem and fixing it, turning a vulnerability into a governed change request and an executed patch deployment without a single manual hand-off. It's change management and endpoint remediation working as one motion instead of two disconnected jobs. If patch cycles have ever felt like a race against the clock, watch how much faster — and safer — that race can be.

"Speaking the Same Language" Tanium Atlas MCP Server: Tanium Tech Talks #169

Want to point your own AI at Tanium? The Atlas MCP Server makes that possible — governed, scoped, and available today. In this episode we cover: Tanium MCP - Available now (read-only) How to set up OAuth clients and how RBAC applies How to scope a single-purpose agent to one module, like Asset, using path-based tool filtering How to tell which tools consume Atlas AI credits - and which don't!

Autonomous Service Desk: A Ticket, Solved Before You Blink

What if your service desk could solve a ticket before a human ever picked it up? Steven Payne walks through a live incident and shows ServiceNow's Now Assist doing the detective work in real time, pulling live Tanium endpoint data to pinpoint the root cause and draft the resolution, all in seconds. No log-diving, no remote sessions, no back-and-forth. Just a faster path from "ticket opened" to "issue resolved," with a person still firmly in control of the final call. This is what an autonomous service desk actually looks like in action — watch it happen.

Real-Time CMDB: The Data Your Automations Can Finally Trust

Most CMDBs are lying to you. The data looks clean, the dashboards look confident, and none of it reflects what's actually running in your environment right now. In this quick walkthrough, Steven Payne shows what happens when Tanium's real-time endpoint truth flows directly into ServiceNow's CMDB — no stale scans, no manual reconciliation, no guessing. Watch asset inventory, software, patch health, and vulnerability exposure snap into focus in real time, and see why "good enough" data is no longer good enough for the automations and AI your business is betting on.