

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code

Insignary Launches Clarity AIR: Closing the Blind Spot Between What Your Developers Declare and What's Actually in Your Code. New snippet-level scanning shows security and compliance leaders which open-source code and which AI-written code never made it into a manifest.
Mend.io upgrades 184 open source organizations to the Renovate Community (OSS) plan

Mend.io has proactively upgraded 184 open source organizations and GitHub users to the Mend Renovate Community (OSS) plan, with no request required. The upgrade covers about 3,000 repositories with roughly 4 million combined GitHub stars. Maintainers get higher resource limits, more concurrency, and access to Merge Confidence.

Open-Source Intelligence Tools for Security Teams

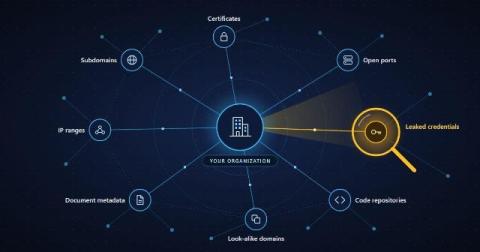
Attackers rarely start with an exploit. They start with a search: which subdomains a company runs, which staff email addresses sit in breach dumps, which forgotten server still answers on the internet. MITRE ATT&CK treats this stage as a tactic of its own, Reconnaissance, and most of it runs on public data.