
Eden Prairie, MN, USA
2012
  |  By Laura Grace Ellis
In the recently released 2026 SANS AI in Cybersecurity Survey, nearly two out of three security professionals said they have been given AI-generated guidance that later turned out to be wrong. Not from an experimental tool off in a sandbox, but from systems built into the security stack they were told to rely on. Security teams should not have to live with that.
  |  By Amy Tierney
AI now plays a central role in defending organizations from the modern threat landscape. It triages alerts, investigates security events, and recommends what to do next. AI is critical to defending at machine speed, but security leaders can’t see how it is making decisions on their behalf. This visibility challenge creates multiple downstream problems for security leaders that need to justify AI decisions that they can’t fully explain to their board, regulatory bodies, and insurance partners.
  |  By Mike McCleary
Imagine this: There’s an active attack but no alert. Nothing looks wrong. Every login is valid. Every tool is trusted. Every command is one your team has run before. This invisible attack chain is how many attackers work today, and they can take control of a domain in minutes and encrypt an environment while evading traditional detections. It’s what happens between the login and the ransom note that’s the modern cyber battlefield.
  |  By Dan Deeth
A lot of the current conversation about agentic SOCs is about triage. Faster detection, faster investigation, alerts resolved in minutes instead of hours. When we set out to build the Aurora Agentic SOC, we didn’t just want to make triage faster. We fundamentally re-engineered our SOC to strengthen every job it does, and enhancing the Concierge Experience for our customers was a key part of that.
  |  By Josh Cronk
New training on using AI safely and spotting AI-powered threats arrives this Cybersecurity Awareness Month Attackers are moving faster than ever, weaponizing newly discovered vulnerabilities before defenders can patch them and building new types of malware that signature-based defenses can’t catch.
  |  By Arctic Wolf Labs
On September 27th 2026, Citrix disclosed multiple vulnerabilities affecting NetScaler ADC and NetScaler Gateway. Arctic Wolf tracking indicates that CVE-2026-88771 and CVE-2026-88772 have been exploited in attacks against NetScaler devices as zero-days. Additional CVEs are also disclosed in the Citrix Security Bulletin. CVE-2026-88771 is an unauthenticated remote code execution vulnerability caused by improper input validation that can allow arbitrary command execution.
  |  By Lisa Tetrault
AI is changing how security operations work. It can process more data, reduce repetitive work, and move investigations forward faster than human teams could on their own. But speed and scale are not the only factors security leaders should be considering. The more important question is what happens to human expertise when machines take on more of the investigative workload. Across the industry, there is growing concern that AI will narrow the path into technical careers.
  |  By Arctic Wolf Labs
A Ukrainian-branded ClickFix lure, a Russian-branded traffic panel, and victims from 32 countries across Europe, the Americas and Asia-Pacific.
  |  By Ankit Jain
The rapid advancement of frontier AI models has fundamentally changed how security products are built. Capabilities that once took months to develop can now be delivered at machine speed, and the market is filling up with agentic security operations centers (SOCs). Numerous vendors now promise AI agents that can investigate alerts, correlate evidence, reason over complex signals, and even close incidents on their own. The technology appears capable, but what often gets left out is a reason to believe it.
  |  By Arctic Wolf
The Arctic Wolf 2026 AI & Cybersecurity Trends Report asked security leaders how much time their teams spend each week on nine separate security tasks, and the answer came back between 13 and 15 hours for each one. That’s a workload that adds up to roughly three full-time people before anything unplanned arrives. Leaders are already acting on the problem.
  |  By Arctic Wolf Networks
Everything is accelerating, and so simply put, if your technologies and your teams aren’t accelerating at the same rate that the threat landscape is, you’re in trouble.” Live from the 2026 Security Operations Summit, Arctic Wolf Chief Revenue Officer Will May joined Monitor the Situation to discuss how security operations are evolving in the age of AI.
  |  By Arctic Wolf Networks
This month we sit down with Devendra Rath, VP of Engineering, as he talks about building and scaling the R&D team in India, how visual thinking shapes his approach to engineering leadership, why he believes AI is a game-changer for software development, and so much more!
  |  By Arctic Wolf Networks
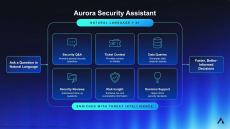
In this demo, we will look at different use cases for the Aurora Security Assistant including the data explorer queries, organizational risk and vulnerability information, and quick answers around self-service and product documentation.
  |  By Arctic Wolf Networks
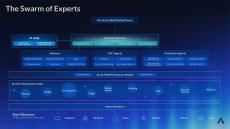
Learn how Arctic Wolf Superintelligence Platform and the Swarm of Experts work together to deliver faster, more accurate outcomes for customers by leveraging unmatched telemetry, deterministic models, our golden data set and human expertise.
  |  By Arctic Wolf Networks
Learn Arctic Wolf's Agentic SOC at scale protects thousands of customers based on one customer alert. In this use case, the network effect enables defenses for thousands of customers against an attack from Payroll Pirate.
  |  By Arctic Wolf Networks
The Howler Podcast is 3! Join Chelsea and Mary as they reflect on the past three years and chat with special guest, Brian NeSmith, Co-founder & Executive Chairman! Interested in running with the pack? Explore careers at Arctic Wolf—one of the fastest-growing and exciting cybersecurity companies in the world, to learn about how you can join our Pack, create impact, and influence what’s next in security operations.
  |  By Arctic Wolf Networks
The volume, velocity, and sophistication of cyber threats continue to grow. Security teams need a new approach. At AWS Security LIVE! during Black Hat USA 2026, Arctic Wolf President & CEO Nick Schneider joined Amazon Web Services' Jess Kubat, Ryan Orsi and Brian Mendenhall for a discussion on security operations at Machine Speed and how organizations can combine AI-powered capabilities with security expertise to stay ahead of modern threats.
  |  By Arctic Wolf Networks
This month, we sit down with Matt Setzer, Senior Vice President, Chief Architect, to learn more about a day in the life of an architect, his philosophy on meaningful innovation, and so much more! Matt Setzer is SVP & Chief Architect at Arctic Wolf, where he partners with product and engineering leadership to set the technical strategy for the Arctic Wolf products and platform. Matt has spent the last twenty years in senior engineering and architect roles in the security space at Microsoft and Sophos. Prior to that he spent number of years working in the game industry.
  |  By Arctic Wolf Networks
Arctic Wolf President of Technology & Services Dan Schiappa sits down for a cocktail chat with Arctic Wolf SVP of Corporate Marketing Ilina Cashiola at Black Hat USA 2026 to break down the momentum behind the Aurora Agentic SOC and what's next for AI-led security operations.
  |  By Arctic Wolf Networks
Arctic Wolf President & CEO Nick Schneider sits down with Ilina Cashiola, SVP of Corporate Marketing, for a cocktail chat at Black Hat USA 2026 to break down three major announcements shaping the next chapter of AI-led security operations.
  |  By Arctic Wolf
Security information and event management (SIEM), security orchestration, automation, and response (SOAR), and the newer extended detection and response (XDR) solutions have become the top choices for organizations wanting a unified view of activity within their IT environments. By combining relevant data into single consoles, XDR, SIEM and SOAR technologies minimize the time analysts spend moving between platforms and make it easier to correlate the data and develop subsequent steps appropriately.
  |  By Arctic Wolf
The Health Insurance Portability and Accountability Act (HIPAA) Security Rule focuses on the safeguarding of electronic protected health information (ePHI) through the implementation of administrative, physical, and technical safeguards.
  |  By Arctic Wolf
Financial institutions, particularly regional banks and credit unions, are facing challenges both in terms of safeguarding data of their customers and meeting data security compliance standards. Information technology (IT) teams in these institutions are stretched thin. They struggle with needing to meet compliance obligations while simultaneously combatting cyberthreats.

Cybersecurity is a field that requires 24x7 vigilance and constant adaptation. Arctic Wolf’s cloud native platform and Concierge Security® Team delivers uniquely effective solutions.

The cybersecurity industry has an effectiveness problem. New technologies, vendors, and solutions emerge every year—yet, we still see headlines filled with high-profile breaches. Many attacks occur – not because a product failed to raise an alert – they fail because the alert was missed or was not actioned on. To prevent these attacks, the industry needs to adopt a new approach by focusing on security operations. That’s where Arctic Wolf can help.

Arctic Wolf® Platform

Spanning thousands of installations, the Arctic Wolf® Platform processes over 200 billion security events daily. The platform collects and enriches endpoint, network, and cloud telemetry, and then analyzes it with multiple detection engines. Machine learning and custom detection rules then deliver personalized protection for your organization.

While other products have limited visibility, the vendor-neutral Arctic Wolf® Platform enables broad visibility and works seamlessly with existing technology stacks, making it easy to adopt while eliminating blind spots and vendor lock-in.

Concierge Security® Team

Arctic Wolf invented the concept of Concierge Security®. With this delivery model, we pair a team of our security operations experts directly with your IT or security staff. Your Concierge Security® Team gives you 24×7 eyes-on-glass coverage. We work with your team on an ongoing basis to learn your security needs so that they can tune solutions for maximum effectiveness and ensure that your security posture gets stronger over time.

The Concierge Security® Team combines deep security operations expertise with an understanding of your environment to deliver better outcomes. We take on tactical actions like threat hunting and alert prioritization, and strategic tasks like security posture reviews and risk management.