On October 21, 2026, Node.js released updates to address multiple vulnerabilities, including an issue in Brotli decoder (CVE-2026-111497). This critical buffer overflow vulnerability (CVSS score of 9.2) has become widely known as Node2Shell but has also been referred to Broccoli2Shell and HTTP2Shell. The issue exists in the Brotli decoder (c/dec/decode.c) in multiple Google Brotli versions, and products that rely on Brotli implementations are vulnerable.
|
By Chris Ahearn
In the world of cyber incident response, experience teaches one truth over and over again: speed matters, precision matters, and coordination matters. But perhaps one of the most overlooked lessons, often learned the hard way, is this: Choosing the right legal counsel is just as critical as selecting the right Digital Forensics and Incident Response (DFIR) firm.
|
By Ratnesh Saxena
SIEM-less security may sound like an escape from traditional SIEM complexity and costs, but the underlying capabilities still have to exist somewhere. A SIEM is a multipurpose tool. It brings together cyber and physical security use cases; drives threat detection, investigation, and response (TDIR); serves as a system of record for governance, regulatory, and compliance needs; and supports observability use cases tied to resilience and service degradation. The list goes on.
In response to requests, this update consolidates the Sophos countermeasures that relate the PHP2Shelll vulnerabilities. SophosLabs has developed the following countermeasures to specifically detect activity associated with this threat. The next table lists additional pre-existing Sophos countermeasures that will likely address post-exploitation activity associated with these vulnerabilities.
|
By Chris Ahearn
Recent incident response investigations reveal how AI-assisted attackers are chaining web application vulnerabilities, credential theft, privilege escalation, and lateral movement into autonomous intrusion workflows. This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI-era threats.
|
By Dan Levesque
This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI-era threats. A 20% growth forecast for cybersecurity talent sounds significant. I believe it understates what we are going to see in Incident Response. The U.S.
The China-based threat group uses DLL sideloading in these attacks Counter Threat Unit (CTU) and SophosLabs researchers investigated a cluster of incidents attributed to the BRONZE SANDCASTLE threat group. The most distinctive technical marker for BRONZE SANDCASTLE is its consistent use of Sandboxie DLL sideloading.
|
By Sophos X-Ops
Automated sign-ins used the vendor's Entra application identity to request Microsoft Graph tokens across consenting tenants On October 15, 2026, Sophos X-Ops researchers identified a series of service principal sign-ins in which a threat actor authenticated as the ConnectWise Cloud Backup application (formerly SkyKick) and requested app-only Microsoft Graph tokens from customer Microsoft 365 tenants.
|
By Andrew Bonwell
Traditional business email compromise (BEC) is often thought of as a mailbox problem: a stolen account, unauthorized access to email, forwarding rules, and (sometimes) outgoing mail impersonating the compromised user. But more recent incidents show how far beyond “email only” these intrusions can extend once an attacker gains control of a cloud identity.
|
By Sophos
Most MSPs act as their customers' CISO, but that work's often informal, unbilled, and hard to repeat. Sophos Fusion CISO Advantage gives you a structured, repeatable framework for cybersecurity posture assessments, transcript analysis, and executive reporting.
|
By Sophos
Mobile devices keep your business moving, but managing them's only half the battle. You've got to secure the users, apps, and business data that depend on them. Sophos Mobile brings mobile device management and mobile threat defense together in one intuitive experience, helping you simplify administration, protect corporate data, and guard users against mobile threats.
|
By Sophos
Sophos Firewall v23 brings new DNS enhancements including DNS-over-HTTPS (DoH) support, DNS security extension (DNSSEC) support, and one-click Secure DNS set up, made possible through native integration with Sophos Fusion. Learn about the new enhancements and the steps to set up Secure DNS Protection, third-party DNS services, and DNSSEC protection. Ask questions and get expert answers in the Sophos Community.
|
By Sophos
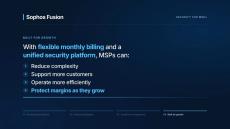
Discover how Sophos Fusion helps Managed Service Providers (MSPs) simplify operations, improve security outcomes, and grow profitability with an AI-native cybersecurity defense system. Chapters Introduction to Sophos Fusion Unified Defense vs. Disconnected Tools Connected Protection Stack (Endpoint, Firewall, Email, MDR, Identity, Network) Shared Intelligence and Unified Response Simplified Management (Multi-tenant, Automation, RMM/PSA Integrations)
|
By Sophos
Discover how Sophos Endpoint’s CryptoGuard technology protects against local and remote ransomware by analyzing data files for malicious encryption and blocking activity automatically.
|
By Sophos
Sophos AI Defense finds the AI tools employees and applications are using, including the ones security teams never approved, and enforces policy wherever they run. Every AI tool an organization can’t see is a potential gap in confidentiality, integrity, and availability. Delivered through Sophos Fusion, the AI-native cybersecurity defense system, Sophos AI Defense connects controls on the device, across the network, at sign-in, and in the browser into one line of defense, so teams can safely adopt AI faster without adding another disconnected tool to manage.
|
By Sophos
Get started with the new REST APIs in Sophos Firewall v23. Learn how to enable API access, authenticate requests with API keys, import the OpenAPI specification into Postman, and use the API to create and manage firewall objects. Ask questions and get expert answers in the Sophos Community.
|
By Sophos
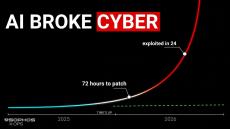
Every defence we rely on assumes there's time to check: verify the person on the call, vet the new hire, review the access request, patch the flaw. This video looks at how AI took that time away, in three parts. Built from the Sophos 2026 AI Security Report.
|
By Sophos
Every defence we rely on assumes there's time to check: verify the person on the call, vet the new hire, review the access request, patch the flaw. This video looks at how AI took that time away, in three parts.
|
By Sophos
You guide the strategy. You recommend the controls. You field the call when something goes wrong. You were always their CISO - now deliver it at scale with Sophos CISO Advantage.
|
By Sophos
This white paper reveals the attack techniques most likely to drive highimpact incidents - and provides practical advice on how to stop them. By learning from realworld attacks, businesses can strengthen their resilience and meaningfully reduce their cyber risk.
|
By Sophos
369 IT and cybersecurity leaders reveal the ransomware realities for financial services providers today. The report examines how the causes and consequences of ransomware attacks on financial services providers have evolved over time. This year's edition also sheds light on previously unexplored areas, including the organizational factors that left providers exposed and the human toll ransomware takes on IT and cybersecurity teams in the financial services sector.
|
By Sophos
Security Operations Centers (SOCs) are essential for detecting and responding to cyber threats, but building the right model isn't one-size-fits-all. With talent shortages and rising threat complexity, many organizations are rethinking how to scale security operations. This guide breaks down the pros, cons, and trade-offs of in-house, hybrid, and outsourced SOC models. Find the SOC strategy that fits your needs, risk profile, and available resources.
- October 2026 (27)
- September 2026 (26)
- August 2026 (8)
- July 2026 (20)
- June 2026 (6)
- May 2026 (25)
- April 2026 (17)
- March 2026 (17)
- February 2026 (6)
- January 2026 (10)
Sophos unites unmatched threat intelligence, adaptive AI, and human expertise in an open platform to stop attacks before they strike — giving you the clarity and confidence to stay ahead of every threat.
Sophos delivers adaptive, AI-powered cybersecurity — backed by real experts — so organizations can stay secure, resilient, and free to grow without compromise.
Sophos advantage in cybersecurity:
- Prevention: Sophos’ approach blocks more threats upfront to minimize risk and reduce investigation and response time.
- Trust: The only vendor named Gartner® Customers’ choice for endpoint, firewalls, mobile threats, and MDR, with 600K+ customers worldwide.
- Platform: Sophos products include 100+ integrations with other third-party solutions, plus services that are highly customizable to your needs.
Take Control of Every Threat