

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Trust Is the New Critical Infrastructure

For more than three decades, cybersecurity innovation and investment have followed a familiar rhythm. Each major wave—network security, endpoint security, identity, cloud, and data—spawned new platform winners and reshaped the M&A landscape. Today, we stand at the threshold of the next foundational shift. The digital and physical worlds have converged to such an extent that machines—not humans—are the primary operators of enterprise networks.
The State of IoT Identity Security in 2026: Why Machine Identity Is the New Perimeter

By 2026, the idea of a fixed security perimeter is no longer realistic. Organisations now operate across cloud platforms, industrial environments, remote sites, and edge locations, often supported by tens or hundreds of thousands of connected devices. These devices are not users in the traditional sense, yet they authenticate, communicate, update, and make decisions autonomously.

IIoT Data Hygiene: How Clean Telemetry Improves Reliability

IIoT data hygiene is the set of operational practices that ensure telemetry remains accurate, timely, and trustworthy for monitoring and analytics. In the rush to connect assets, teams often overlook the quality of the data stream itself, leading to noisy alerts and unreliable models. This article focuses on practical actions Ops teams can implement with low risk and limited engineering effort.

Digital Signage Security: The IoT Vulnerability Hiding in Plain Sight

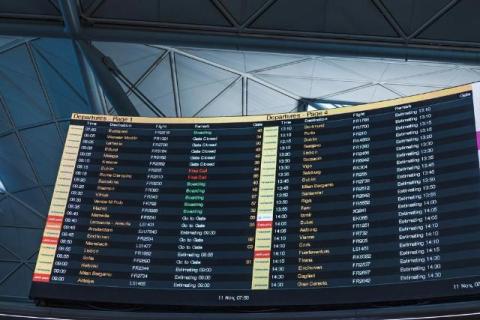
Walk through any airport terminal, hospital corridor, or corporate lobby, and you will encounter digital signage displays. They announce flight departures, guide patients to their appointments, and broadcast company news to employees. These screens have become so common that we barely notice them anymore. And that invisibility is precisely the problem. While cybersecurity teams focus their attention on firewalls, endpoint protection, and cloud security, digital signage systems often slip under the radar as low-priority assets. Hackers, however, have taken notice.

WP 29 Automotive Cybersecurity and Beyond - How India and China Are Now Driving Global Trends

When UNECE WP.29 came into force, it transformed the global automotive industry. For the first time, cybersecurity became a mandatory requirement for modern vehicles — not a marketing feature, not a technical add-on, but a regulated obligation. WP.29 forced manufacturers to rethink how vehicles were designed, updated and secured, requiring formal Cybersecurity Management Systems (CSMS) and Software Update Management Systems (SUMS) across the entire vehicle lifecycle.