Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

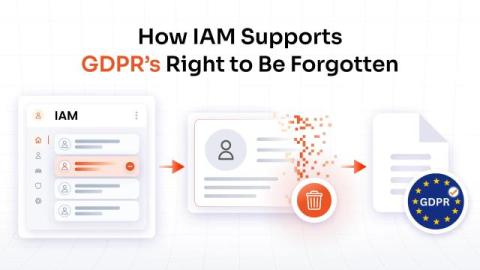
How IAM Supports GDPR's Right to Be Forgotten

Deleting a user account takes seconds. Deleting everything your organization knows about that user is a much bigger job. When a customer invokes their right to be forgotten, their profile in your identity provider is only the starting point, because their details also live in your CRM, support desk, billing tool, analytics platform, and a few SaaS apps your marketing team connected last year. Every one of those copies has to be found and dealt with before the legal deadline.
The EU Cyber Resilience Act puts product makers on a 24-hour clock

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

CIPA for websites in 2027: what the law still covers, and how to show what your site does

If people in California use your website or app, assume CIPA applies. CIPA was written for telephone wiretapping, and courts have applied its "technology-neutral" terms to online communications for years. The business's location does not matter; the visitor's does.

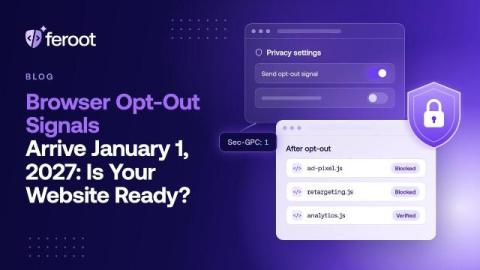
Browser opt-out signals arrive at scale on January 1, 2027. Here is how to know your site honors them.

If the CCPA covers your business, you must treat an opt-out preference signal as a valid request to opt out of the sale or sharing of personal information. "Sharing" includes disclosures for cross-context behavioral advertising, which is what most advertising pixels do.