Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Productiv shutdown: Switch to 1Password for durable AI and SaaS Management

On August 2, 2026, Productiv told customers its SaaS management platform was shutting down on August 6, with account data deleted once access ended. Four days is not much time to pull years of app inventory, spend, and usage data out of a system you've come to depend on, especially with AI tools now adding a fast-moving new layer of spend and access to track on top of everything else.

How CFOs can manage AI costs and prove business value

Earlier this year, a bill arrived from one of 1Password’s AI vendors for 5x the value of the original contract. The initial agreement came in below a certain threshold, so it never reached the right approvers for review. By the time it did, we had a much clearer understanding of how quickly AI costs can add up.

The 1Password Environments MCP Server is now on Cursor Marketplace

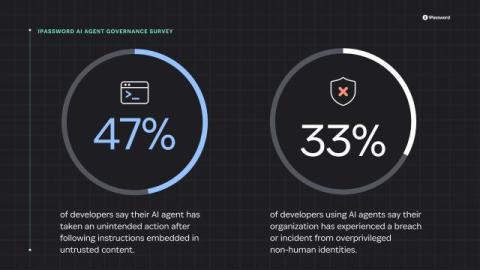
AI agents are doing more than just generating code. Increasingly, they are working autonomously on complex coding challenges, touching production APIs, databases, and infrastructure across development environments, often without thorough human review. To perform these operations and access multiple systems, agents rely on developer secrets and non-human identities (NHI). But often, developers lack a secure way to share these secrets, leading to overprivileged, invisible access.

Scaling security reviews at 1Password: Solving the context and nondeterminism problems

In our last post, we shared how we began to scale our security code review process with SAGE. We discussed how we gathered historical Product Security (ProdSec) review records to create a 1Password-specific ruleset, the three-stage Finder/Critic/Judge pipeline, and the limitations of our v1 implementation.

1Password Credential Broker is now in public preview

Every security team has tried to trace a credential access event back to a specific workload, and received nothing but a "service account." That service account probably had access to an entire vault, and its audit trail doesn’t tell you which repo triggered the request, which specific credential was accessed, or whether the workflow still has access. When an auditor asks, or an incident occurs, that's not a good place to be.

Delegated authority, running locally: Give an agent on your machine an identity you can trust

Part 3 of our agent-identity series: a reference architecture showing how a locally running AI agent, like the coding assistant in your editor or the copilot in your browser, can borrow a human's authority in a scoped, short-lived, auditable way, anchored in an app the user already trusts.