In an era when AI lets attackers blend in and move at machine speed, Tanium Security Operations detects by behavior, responds at scale, and makes expert hunting routine for every analyst.
The Service Graph Connector for Tanium has been a reliable and proven way ServiceNow customers keep their CMDB populated with Tanium endpoint data. As environments have grown and AI has accelerated the pace of change, the opportunity became clear: what if the CMDB could reflect that change as it happens, instead of catching up on a schedule?
The Hunt or be Hunted series tells the hunt stories. HuntIQ Tradecraft, now live on the Tanium Resource Center, gives you the playbooks to run them yourself.
Tanium’s customers span critical infrastructure sectors, including some of the largest banks, hospital systems, and government agencies in the world. They trust our agent on their most sensitive endpoints, which means that the software we ship must meet the high standards they set for themselves. That’s why we hunt our own vulnerabilities before anyone else can.
A hunting playbook built for ClickFix went looking for pasted commands and found a working credential to a third-party portal instead. Here is the sensor question, the filtering logic, and the reason keyword hunting fails at this.
Sweep your entire Windows estate for a public CrowdStrike Falcon Zero-day in about a minute, from one prompt. Here's how Tanium HuntIQ threat hunters built the hunt. No vendor patch required.
On August 11, 2026, a security researcher publicly released a proof-of-concept called ShieldBreak, a full bypass of Microsoft’s own July patch (RoguePlanet) for a Windows Defender privilege-escalation flaw, with a reported 100% success rate against Windows 11 25H2 and Windows Server 2025. No vendor fix existed for the bypass. The only real defense was whoever moved first.
Along with the Bank of England in May, the ECB is requiring organisations to produce an action plan against AI-driven cyberattacks (opens in a new tab). What it wants, however, is not a strategy paper but proof of operational readiness.
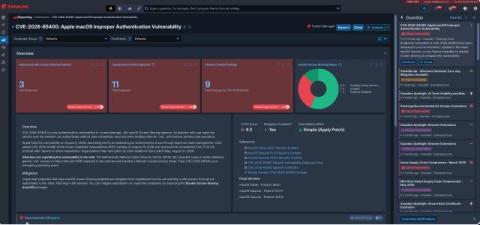
On August 6, 2026, Apple shipped an emergency, out-of-band fix for CVE-2026-65400, an authentication issue in screensharingd, the daemon behind Screen Sharing, macOS's built-in remote desktop service that listens on TCP port 5900. Apple's advisory describes an attacker who could reach the service over the network and authenticate without valid credentials, then read and write files as root—enough to achieve full remote code execution.
Security teams don't have a shortage of data. They have a shortage of time, repeatability, and senior expertise available at the exact moment an analyst needs it. That's the problem Atlas slash commands are designed to solve. With /hunt, /investigate, and /signal, Atlas turns a simple chat interaction into a guided SecOps workflow grounded in live endpoint state.