Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

ShieldBreak: The Windows Defender 0-Day with No Patch - And What to Do About It.

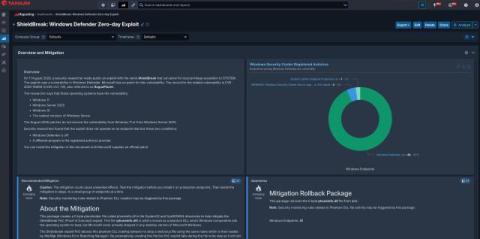
In mid-June 2026, Microsoft acknowledged RoguePlanet, a privilege-escalation flaw in the Microsoft Malware Protection Engine (mpengine.dll), the scanning engine behind Windows Defender. Microsoft rated it "Exploitation More Likely" on its Exploitability Index and assigned a CVSS score of 7.8. Microsoft shipped a fix in Malware Protection Engine version 1.1.26060.3008 during its July 2026 patch cycle.
AI Is Accelerating Vulnerability Discovery. Tanium Helps You Keep Up.

Following the Mythos announcement in April 2026, organizations using AI to identify software vulnerabilities have contributed to a significant rise in newly discovered CVEs and CVE definitions. This shift reflects a broader trend across the industry: AI is helping uncover vulnerabilities faster than ever before — and security teams need the visibility, control, and speed to respond. At Tanium, we've been tracking this trend closely across customer environments.

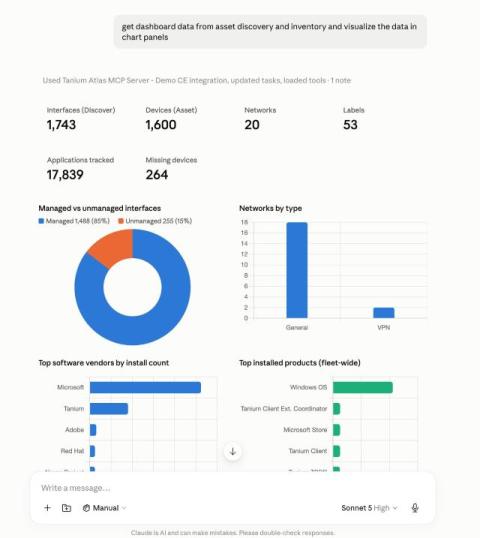
Bringing Tanium's real-time endpoint intelligence into enterprise AI workflows with MCP

Enterprise AI is quickly moving from experimentation to day-to-day operational use. Security analysts, IT operators, and platform teams are increasingly working inside AI-native environments — from Claude and Microsoft Copilot experiences to internally built agents and automation workflows. But there is a practical challenge: AI workflows are only as useful as the enterprise systems they can safely reach.

Introducing Agentic SecOps: Live Endpoint Truth for the AI-Driven SOC

Security operations teams are being asked to move faster than ever. Adversaries are using automation, infrastructure changes by the minute, and the number of alerts, exposures, and investigative paths keeps growing. But too many SOC workflows still depend on scarce expert time. A senior analyst writes the query, translates the hypothesis, pivots across tools, validates the result, and then hands the finding off for action. The craft works.

Tanium and Google Threat Intelligence bring Google-grade threat intel to the live endpoint

Security teams are under pressure to move faster, investigate more confidently, and make better decisions with fewer resources. But even the best security operations teams run into the same problem. They often do not have a reliable place to start. Threat hunting depends on high-quality intelligence and experienced analysts who know how to turn that intelligence into useful pivots. Alert triage depends on knowing which signals matter and which ones are noise.

Security automation tools: What they are and how they work

Security automation tools use software-driven workflows to detect, investigate, and remediate cyberthreats with minimal manual intervention. By integrating across your security stack, these tools reduce alert fatigue, accelerate automated incident response, and maintain continuous compliance.

Building an effective endpoint security strategy in 2026

An endpoint security strategy is a structured plan that defines how an organization protects, monitors, and manages all devices connecting to its network (including laptops, desktops, servers, mobile devices, cloud workloads, and OT systems) through coordinated policies for access control, threat detection, vulnerability management, and incident response.

Continuous vulnerability management: Is your program actually continuous?

Continuous vulnerability management (CVM) is an ongoing, automated approach to discovering, analyzing, prioritizing, and remediating security weaknesses across an organization's IT environment. It replaces periodic scans with real-time visibility that shrinks attacker opportunity windows.