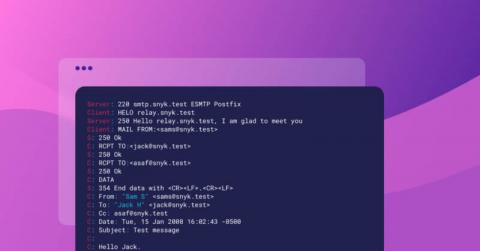
SMTP Injection vulnerabilities are often misunderstood by developers and security professionals, and missed by static analysis products. This blog will discuss how common SMTP Injection vulnerabilities can exist in libraries and applications, and provide tips for finding and remediating them quickly.
September 14, 2022: Check out our new and improved cheat sheet for containerizing Node.js web applications with Docker! Are you looking for best practices on how to build Node.js Docker images for your web applications? Then you’ve come to the right place! The following article provides production-grade guidelines for building optimized and secure Node.js Docker images. You’ll find it helpful regardless of the Node.js application you aim to build.
Cloud computing has created the most profound shift in information technology in recent memory. Leveraging cloud technology, companies can build, deploy, and scale their applications faster than ever. But the adoption of cloud native tools and processes also brings new security challenges. Between complex cloud infrastructure and the expansion of cloud-based services, malicious actors have access to a bigger attack surface than they did even a few years ago.
Spotify’s engineering team recently published a blog discussing their use of Snyk to maintain security testing in the SDLC. The following is a recap of that blog written by Engineering Manager, Edina Muminovic. Spotify, a company known for employing thousands of world-class developers, needed to redraw its software development lifecycle, or SDLC.
Technology is always changing and your processes and practices need to keep up with those changes. So while npm is 12 years old, your practices around npm package creation should hopefully be a lot more modern. If you have a feeling they may be a little out of date, though, keep reading.
Onna Technologies, a data centralization software company, integrates security across every facet of their development process by using Snyk and Sysdig. We recently sat down with Onna’s Brent Neal (Director of Security), Mike Hoffman (Lead Security Engineer), and Andrew Leeb (Senior Software Engineer) to discuss data protection and compliance, cloud security priorities, and the benefits using Snyk and Sysdig for complete end-to-end container security.
ConfigMaps is an API object used in Kubernetes to store data in key-value pairs. It’s essentially a dictionary that contains configuration settings. Some details you might expect to find in a ConfigMap include hostnames, public credentials, connection strings, and URLs. A ConfigMap decouples an application’s code from the configurations, making it possible to alter them without impacting the application.