Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

DevSecOps Road Trip Netherlands stop - Nanne Baars & Brian Vermeer

Session 1: From attack to writing code...what do you need to know as a developer? We will look at a concrete attack called: "XML external entity attack (XXE)" and see how we can trace it back to writing code. The described mitigations are simple: configure your parser securely, but is it this simple? We will focus on some examples and see if we can catch the attack with tests, code reviews, etc. Nanne Baars, Developer at Xebia and OWASP WebGoat Project lead
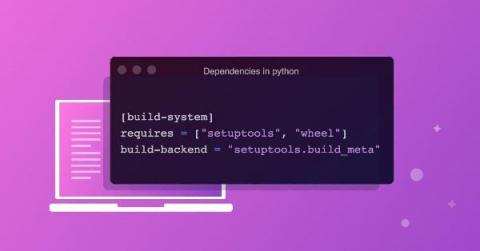
A (soft) introduction to Python dependency management

Python has been deemed as a “simple” language — easy to use and easy to develop scripts to do numerous tasks — from web scraping to automation to building large-scale web applications and even performing data science. However, dependencies are managed quite differently in Python than in other languages, and the myriad options of setting up an environment and package managers only add to the confusion.

DevSecOps Road Trip UK stop - Andrew Martin & Lili Kastilio

Session 1: Threat Modelling Kubernetes Cloud native container and Kubernetes systems bring new threats and risks to our precious workloads. As cloud technologies undergo rapid innovation and new tools and techniques emerge, security can get left behind. The answer to this conveyor-belt of potential insecurity? Threat modelling!

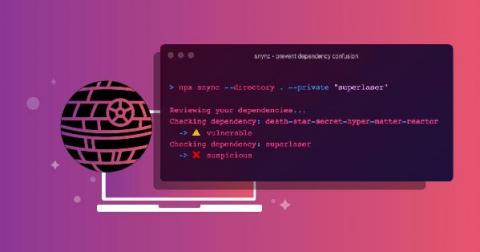
Detect and prevent dependency confusion attacks on npm to maintain supply chain security

On February 9, 2021, Alex Birsan disclosed his aptly named security research, dependency confusion. In his disclosure, he describes how a novel supply chain attack that exploits misconfiguration by developers, as well as design flaws of numerous package managers in the open source language-based software ecosystems, allowed him to gain access and exfiltrate data from companies such as Yelp, Tesla, Apple, Microsoft, and others.