Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Scaling security reviews at 1Password: Solving the context and nondeterminism problems

In our last post, we shared how we began to scale our security code review process with SAGE. We discussed how we gathered historical Product Security (ProdSec) review records to create a 1Password-specific ruleset, the three-stage Finder/Critic/Judge pipeline, and the limitations of our v1 implementation.
1Password Credential Broker is now in public preview

Every security team has tried to trace a credential access event back to a specific workload, and received nothing but a "service account." That service account probably had access to an entire vault, and its audit trail doesn’t tell you which repo triggered the request, which specific credential was accessed, or whether the workflow still has access. When an auditor asks, or an incident occurs, that's not a good place to be.

Secrets Off Disk: How 1Password Secures Developer Workflows

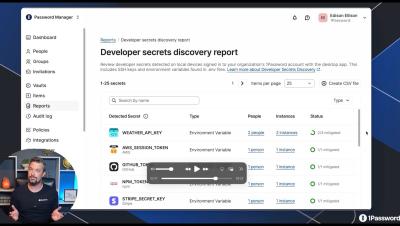
Your.env file has your database password, your AWS keys, and your Stripe secret, all in plaintext, sitting on your laptop. 1Password Developer Watchtower finds it, 1Password Environments secures it, and you keep shipping. See how 1Password discovers plaintext developer credentials, imports them into an encrypted environment, and mounts a virtual protected.env, with no workflow disruption for developers and full fleet visibility for security teams.

Distributed systems in disguise with Maxim Fateev from Temporal | Zero-Shot Learning

When most developers write code, crash recovery logic is at the bottom of their priorities, until crashes and delays force them to incorporate resiliency logic. That’s why Temporal co-founder and CTO Maxim Fateev built a system to turn code into durable execution. In his conversation with 1Password CTO Nancy Wang and VP of Engineering for Developer and AI Jeff Malnick, Maxim explains why the distributed systems thinking that shaped his work is now essential for building reliable AI agents, with a live demo of a durable agent surviving a crash.

Delegated authority, running locally: Give an agent on your machine an identity you can trust

Part 3 of our agent-identity series: a reference architecture showing how a locally running AI agent, like the coding assistant in your editor or the copilot in your browser, can borrow a human's authority in a scoped, short-lived, auditable way, anchored in an app the user already trusts.

The tokenmaxxing bill is due: Take control of AI spend with SaaS Manager

A nasty shock is hitting finance leaders across every industry right now: AI token bills that run ten, twenty, even a hundred times over what they forecasted, blowing holes straight through quarterly budgets. These leaders are all asking the same questions: How could this happen if they didn't approve it? Why didn't any of their systems alert them to the spike? And most importantly, what can they do now?