

Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is Red Teaming? - A Cyber Security Methodology

Red Teaming is a cyber security methodology that uses simulations and attacks to identify an organization's vulnerabilities. In this video, we explore what red teaming is, how it works, and some of the benefits it can provide.#redteaming #cybersecurity Cyphere is a UK-based cyber security services provider helping organisations to secure their most prized assets. We provide technical risk assessment (pen testing/ethical hacking) and managed security services. This advice is a true third party opinion, free from any vendor inclinations or reselling objectives.
Red, Purple, and Blue: The Colors of a Successful Cybersecurity Testing Program

This is the first in a series of blogs that will describe the importance of conducting Red and Purple Team exercises. The first entry in the series gives an overview of how to properly conduct these drills with follow on blogs diving deeper into the specifics of Red and Purple team maneuvers. The first realization most organizations have that their cybersecurity is, let's say, subpar generally comes right after it has been hit by a devastating attack.

Red Team: O365 MFA Bypass To Device Compromise

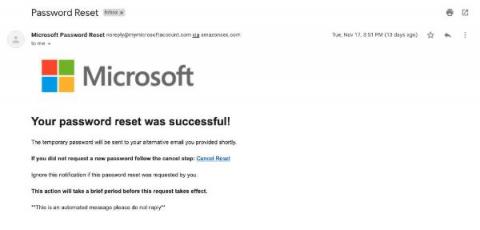
The array of phishing vectors used by attackers is constantly expanding. On a daily basis we observe numerous different phishing themes such as voicemails, fake invoices and documents requiring signing. Recently, we have seen more topical themes such as US elections, COVID-19 and Brexit.

How does Red Teaming differ from a Penetration Test?

JUMPSEC Jargon Buster - Nikoo explains how Red Teaming differs from a Penetration Test. There are a number of ways that a red teaming exercise differentiate from a pen test. Firstly, the scope of standard penetration test is usually clearly defined with the goal to identify as many vulnerabilities as possible and attempt to exploit them on the stated targets during the engagement.