Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is AI system prompt hardening?

As generative AI tools like ChatGPT, Claude, and others become increasingly integrated into enterprise workflows, a new security imperative has emerged: system prompt hardening. A system prompt is a set of instructions given to an AI model that defines its role, behavior, tone, and constraints for a session. It sets the foundation for how the model responds to user input and remains active throughout the conversation.
Real-Time Image Switching: Upgrade Without Downtime! Tech Tip #podcast #tech

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

AI Voice Mimicry: How to Protect Yourself From Scams #appsec #cybersecurity

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

Fixing 4,000 Vulnerabilities? Quick Ways to Eliminate Security Issues! #podcast #infosec

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

SCA Tool: Why Developers Love It & Boost ROI Instantly!

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

From Reactive to Proactive AppSec: Your Security Team's Secret Weapon! #cybersecurity

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

Secure Your Data: Get Executives On Board for Better Security #cybersecurity

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

Why Keeping Old Software Is a Security Risk #cybersecurity #appsec

Mend.io, formerly known as Whitesource, has over a decade of experience helping global organizations build world-class AppSec programs that reduce risk and accelerate development -– using tools built into the technologies that software and security teams already love. Our automated technology protects organizations from supply chain and malicious package attacks, vulnerabilities in open source and custom code, and open-source license risks.

Risk Mitigation and Cybersecurity Strategy with Samuel Brown | Secrets of AppSec Champions Podcast

As cyber threats evolve, so must the strategies to prevent them. In this episode, Samuel Brown—CEO of PacketX and retired U.S. Army CW4—shares mission-critical insights on risk mitigation, layered security, and why backups and plans on paper aren't enough. From ransomware recovery to real-world network defense, this conversation is packed with hard-earned lessons for AppSec professionals and business leaders alike.

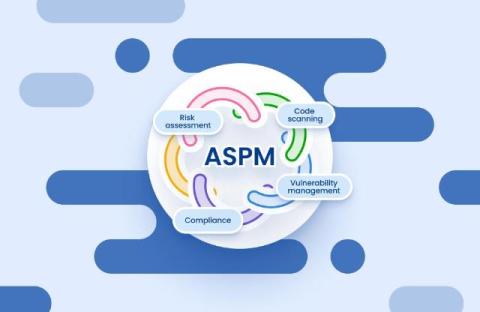
What Is Application Security Posture Management (ASPM)?

Application security posture management (ASPM) centralizes and automates the monitoring, evaluation, and management of application security across an organization’s software lifecycle. ASPM provides a unified view of the risk posture by aggregating data from various security tools, such as static application security testing (SAST), dynamic application security testing (DAST), software composition analysis (SCA), and runtime protection solutions.