Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Mend Renovate Enterprise Cloud: Dependency Updates at Scale

If there’s one thing development and security teams can agree on, it’s that updating dependencies is a worthwhile endeavor. Keeping open-source dependencies up to date reduces bugs—both now and in the long run. And whether those bugs are security vulnerabilities or functional issues, everyone is happy to see them go.
CVSS 3.1 vs CVSS 4.0: A Look at the Data

Like the cost of groceries and everything else, CVSS scores seem to have experienced some inflation recently. CVSS 4.0 promises to be a better calculator of risk than previous iterations of the system, but that’s only true if you use it in its full capacity to calculate your specific risk within your specific environment. Most of us aren’t using it that way.

Mend.io - Backstage Integration: Bringing Security Insights Where You Need Them

Launched as an internal project by Spotify in 2016, Backstage was released under the Apache 2.0 open source license in 2020 to help other growing engineering teams deal with similar challenges. Backstage aims to provide a consistent developer experience and centralize tools, documentation, and services within a single platform.

The @Solana/web3.js Incident: Another Wake-Up Call for Supply Chain Security

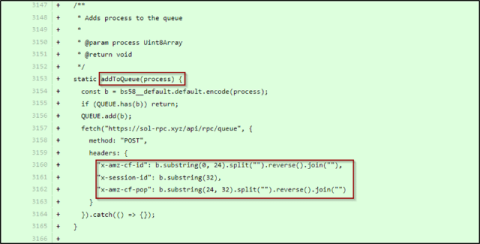
On December 2, 2024, the Solana community faced a significant security incident involving the @solana/web3.js npm package, a critical library for developers building on the Solana blockchain with over 450K weekly downloads. This blog post aims to break down the attack flow, explore how it happened, and discuss the importance of supply chain security.

Mend.io is a Strong Performer in the Forrester Wave Software Composition Analysis, Q4 2024

It should be no surprise that the world runs on open source software. According to the latest Forrester Wave Software Composition Analysis Q4 2024 report an “astonishing 77% of codebases are comprised of open-source software.” Since a “considerable amount of an application’s risk is due to third-party sources,” software composition analysis (SCA) tools remain the lifeblood for securing modern applications and bringing greater transparency to the software supply chain.

All About RAG: What It Is and How to Keep It Secure

AI is growing in power and scope and many organizations have moved on from “simply” training models. In this blog, we will cover a common system of LLM use called Retrieval-Augmented Generation (RAG). RAG adds some extra steps to typical use of a large language model (LLM) so that instead of working off just the prompt and its training data, the LLM has additional, usually more up-to-date, data “fresh in mind”.

Vital Signs of Software Dependencies: Understanding Package Health

As the vast majority of modern applications rely heavily on open-source software, dealing with updates for dependencies can become a major hassle for both developers and cybersecurity professionals. Every developer knows the pain of an update breaking their application. Manually determining which dependencies to run can become a massive time-suck, which is why many developers fall behind on updates, leaving applications open to vulnerabilities.

Cybersecurity Awareness Month: AI Safety for Friends and Family

Happy October! The leaves are changing and everyone is starting to get ready for the upcoming holidays, but let’s not forget one of the most important holidays of the year—Cybersecurity Awareness Month! Though our audience is almost entirely cybersecurity experts, we wanted to put something together to help the less technical people in our lives learn more about AI and cybersecurity, because Cybersecurity Month is for everyone.