Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

LevelBlue Threat Hunters Earn Top Global Rankings in SentinelOne Competition

Three LevelBlue security experts put their investigative skills to the test in the SentinelOne Threat Hunting competition, with Jodie McDonald earning the top spot in EMEA and advancing to the Grand Final at OneCon. Threat hunting requires more than knowing your way around a security platform. It takes curiosity, analytical thinking, and the discipline to follow the evidence, even when it leads somewhere unexpected.
LevelBlue Named Frost & Sullivan's 2026 Global Company of the Year in Managed Security Services

Security teams face a demanding balancing act: keeping pace with evolving threats, managing complex environments, and demonstrating how their investments reduce risk. At LevelBlue, helping organizations meet those challenges is central to our work. That commitment is reflected in Frost & Sullivan’s recognition of LevelBlue as its 2026 Global Company of the Year in Managed Security Services.

Acronis expands MDR toward broader workspace protection

Cyberattacks do not respect normal business hours: They can happen at night, on weekends and during holidays. Acronis MDR by Acronis TRU gives partners 24/7/365 expert monitoring, investigation and response without having to build their own security operations center (SOC). Acronis is expanding the MDR service with capabilities that make this expertise easier to deliver and help partners address more risks. The developments build on a broader commitment to managed security.

CrowdStrike Named a Leader in the 2026 IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises Vendor Assessment

CrowdStrike has been named a Leader in the 2026 IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises Vendor Assessment. We believe this recognition reflects the strength of the CrowdStrike Falcon platform and the proven endpoint capabilities CrowdStrike brings into the AI era: industry-leading protection at scale, consistent analyst recognition, measurable business value, and the trust of customers globally.

Sophos Named a Leader in the IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises 2026

Sophos has been named a Leader in the IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises 2026, recognizing the strength of our prevention-first approach and stopping AI-era threats as early as possible. Attackers using frontier AI models can now find vulnerabilities and generate exploits faster than organizations can patch them. And when malicious code is already running before an alert fires, detection alone is too late.

Acronis Cyber Protect Cloud earns maximum score in AV-TEST Advanced Threat Protection test

Author: Alexander Ivanyuk Advanced attacks often use trusted Windows components and legitimate-looking files to conceal malicious activity. A manipulated DLL can run through a signed executable, while a scheduled task can launch PowerShell to load harmful code. These techniques make independent testing valuable because a security product must recognize the attack chain, not only a suspicious file.

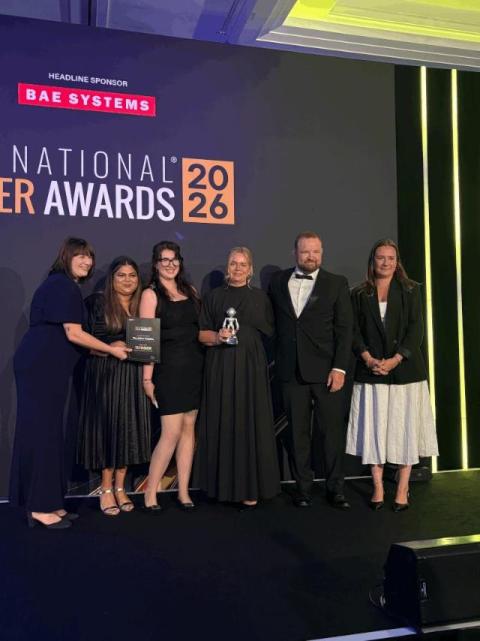
The Cyber Helpline Wins Not-for-Profit Award at 2026 National Cyber Awards

London, UK, September 29th, 2026 – We are thrilled to announce that The Cyber Helpline has been named Not-for-Profit Cyber Award winner at this year's National Cyber Awards. This marks our fifth win in the category, following wins in 2021, 2022, 2023 and 2024. Our team and volunteers were also recognised as finalists in three further categories: the Alan Turing Cyber Leadership Award, the Cyber Diversity Award and the Cyber Student of the Year Award.

Detectify positioned as a Major Player in the IDC MarketScape for Worldwide Dynamic Application Security Testing

When modern development teams and AI agents ship code at unprecedented speeds, the runtime security checkpoint becomes an indispensable line of defense. However, far too many AppSec teams find themselves drowning in a sea of false positives, overburdened by legacy tools that infer potential vulnerabilities rather than proving their real-world exploitability.