Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Security Control Management: The New Mandate for Risk-Driven Security

Article updated and refreshed February 3rd, 2026. Because the tools you’ve deployed aren’t the same as the ones you’re using. Security teams today aren’t short on tools. Most environments are packed with security controls—spanning email, identity, network, endpoint, and cloud. But despite this abundance, risk remains stubbornly high. Attacks continue to land. Exposure persists. The problem isn’t the absence of controls. It’s the lack of control over the controls.
What is Security Optimization? How to Find Gaps in Your Stack

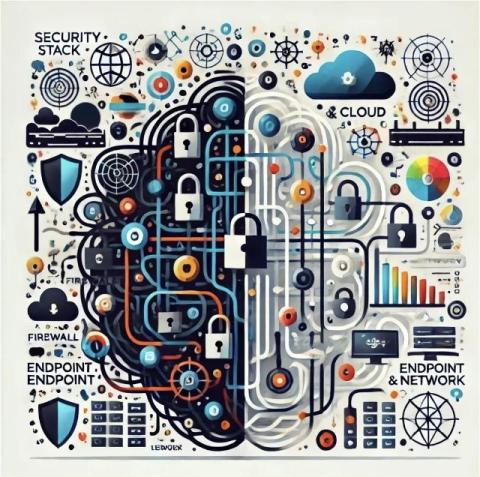
Organizations invest heavily in security tools, yet many still struggle with underutilized capabilities, misconfigured controls, and fragmented visibility. Simply adding more tools doesn’t guarantee better security. In fact, it often leads to overlapping functionality, increased operational complexity, and wasted resources.
Featured Post

AI for Security Infrastructure: Rebalancing Cybersecurity for the Decade Ahead

For more than a decade, cybersecurity has been shaped by a single doctrine: assume breach. Facing high-volume, relentless, and diverse attacks, the security industry has been forced into a reactive stance, playing a constant game of whack-a-mole in a nonstop damage-limitation exercise. This has driven major investment in detection, response, and recovery, and created a world in which organizations are better at reacting to incidents than at preventing them in the first place.

Reach Security Recognized as a Representative Provider of ASCA in the Gartner Innovation Insight: Automated Security Control Assessment

In its January 2026 research report, Innovation Insight: Automated Security Control Assessment, Gartner discusses why misconfigured security controls remain one of the most persistent drivers of breaches and why automation is now required to address the problem at scale.

What Device Code Phishing Reveals About Security Configuration Gaps

Recent research from Proofpoint highlights a growing trend in identity-based attacks. Rather than stealing passwords or exploiting software flaws, multiple threat actors are now abusing legitimate Microsoft authentication workflows to gain access to Microsoft 365 accounts at scale. This technique, known as device code phishing, is not new. What is new is how widespread the technique has become, particularly among both state-aligned and financially motivated adversaries.

When Misconfigurations Become the Front Door: What Russia's Edge Device Campaign Signals for Modern Cyber Defense

A recent Dark Reading article highlighted a sobering shift in how nation-state threat actors are gaining access to critical infrastructure. According to reporting on a new Amazon Threat Intelligence disclosure, Russian actors affiliated with the GRU have spent years refining a campaign that increasingly bypasses traditional vulnerability exploitation altogether. Instead, they are walking straight through the front door left open by misconfigured network edge devices.

Reach Security Joins the Microsoft for Startups Pegasus Program to Accelerate Agentic AI for E3/E5 Security Optimization

Reach Security announces its acceptance into the Microsoft for Startups Pegasus Program. Through the Pegasus Program, Reach will collaborate with Microsoft to help enterprise customers optimize their use of Microsoft E3 and E5 security suites by addressing configuration, visibility, and operational gaps through agentic AI.

Threat Exposure Management: A Better Way to Answer "How Exposed Are We?"

Security leaders are asking a new question with greater urgency: How exposed are we? In an era where every application, identity, and integration expands the attack surface, answering that question with clarity is no longer optional. The traditional model of vulnerability management cannot keep up. Findings come in faster than they can be addressed. Visibility is fragmented. Risk prioritization is often based on severity scores rather than business impact.
Featured Post

My Black Friday Cybersecurity Wishlist

Black Friday and Cyber Monday always bring bargain buys as consumers hunt for deals to make the upcoming festive season special, but they are also a bonanza for cybercriminals. Attacks spike during the holiday season as cybercriminals take advantage of workers being out of their usual routine and less vigilant than normal. This makes for far from happy holidays for the businesses affected. However, what many organizations don't realize is that often they already have the tools to protect themselves in their security armory; they just haven't activated them.