The 2010 Stuxnet malicious software attack on a uranium enrichment plant in Iran had all the twists and turns of a spy thriller. The plant was air gapped (not connected to the internet) so it couldn’t be targeted directly by an outsider. Instead, the attackers infected five of the plant’s partner organizations, hoping that an engineer from one of them would unknowingly introduce the malware to the network via a thumb drive.
Detecting and preventing malicious activity such as botnet attacks is a critical area of focus for threat intel analysts, security operators, and threat hunters. Taking up the Mozi botnet as a case study, this blog post demonstrates how to use open source tools, analytical processes, and the Elastic Stack to perform analysis and enrichment of collected data irrespective of the campaign.
Kubernetes helps with scaling, deploying, and managing containerized workloads, facilitating a faster deployment cycle and configuration management—all while providing improved access control.Kubernetes is also a CNCF project, meaning it’s cloud-native and can be easily deployed through any cloud provider. This blog will compare on-premises, or self-hosted,Kubernetes clusters to managed ones, as well as outline your options for Kubernetes in the cloud.
Deploying a SIEM requires strategic planning. When deciding on a deployment, an organization must consider the level of risk it is willing to assume, what its security priorities are, and which use cases to implement. From there, your security operations team must thoughtfully identify their inputs — the data the SIEM solution will gather — before rolling out anything. Otherwise, you won’t obtain your desired outputs to identify high-fidelity alerts to act on.
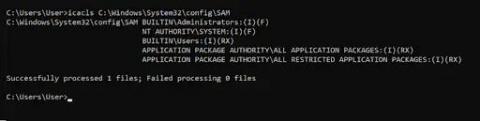
SeriousSAM or CVE-2021-36934 is a Privilege Escalation Vulnerability, which allows overly permissive Access Control Lists (ACLs) that provide low privileged users read access to privileged system files including the Security Accounts Manager (SAM) database. The SAM database stores users' encrypted passwords in a Windows system. According to the Microsoft advisory, this issue affects Windows 10 1809 and above as well as certain versions of Server 2019.
Vonahi Security, as a member of the cybersecurity community committed to the prevention of all forms of harassment within our industry, hereby pledges its support for a workplace and community free from harassment and fear.
Although the Sarbanes-Oxley Act of 2002 (SOX) has been around for nearly two decades, many companies still struggle to meet compliance requirements. Initially enacted in response to public companies mishandling financial reporting, SOX is a compliance requirement for all public companies. Understanding SOX compliance, as well as its requirements and controls, helps organizations create more robust governance processes.
As organizations look for ways to improve network performance for user-facing application data, it is becoming increasingly evident that routing requests all the way to internal data centers is the least optimized model. Doing so increases latency, reduces available bandwidth, increases bandwidth requirements at the data center, and increases overall costs.