Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Wait, Did We Just Invent Classifiers Again? Introducing Jev, a new way to do AI.

For the last few years, when somebody says “AI,” what they are usually referring to is a Large Language Model, or LLM for short. You chuck some text in, it has a think, and it gives you some more text back. This is brilliant if you want code written, documents summarised, or quantum physics explained to you in a limerick, but while this is great for humans, most software doesn’t actually want a beautifully written paragraph. Software just wants an answer so it can make a decision.
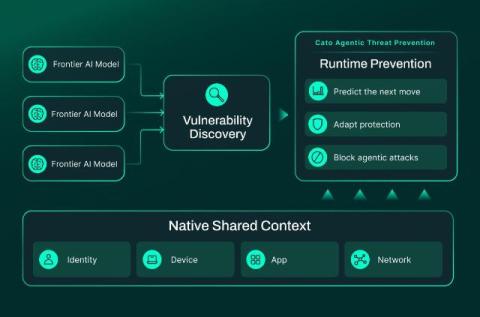
Beyond Model Access: Frontier AI Defense Needs Runtime Prevention

Access to powerful AI models is opening new possibilities for cybersecurity. Models can help uncover weaknesses, investigate threats, and explore how attackers might break into an environment. Using several models can bring different strengths to that work. But model access alone does not answer a critical question: can your defense stop an attack while it is happening? In the frontier AI era, discovery needs to connect to action.

Why a clean firewall policy isn't enough to secure your network

Your last firewall audit came back clean. Every rule documented, every exception justified, every box checked, exactly what PCI DSS and your other compliance frameworks and attestations require. None of that tells you whether a compromised laptop in marketing can actually reach your payment systems right now. The audit verifies your firewall policy. It was never built to verify your network.

Understanding Asymmetric Routing Risks in Modern Firewall Deployments

In modern network environments, maintaining both operational efficiency and strong security controls requires careful design and planning. One of the more common challenges Sophos Professional Services encounters, especially during firewall upgrades or redesigns, is asymmetric routing.

Strengthening Network Security for Modern Organizations

Organizations today face a common challenge: networks are growing, wireless connectivity is supporting more users and devices, and security threats continue to evolve. At the same time, IT teams are expected to deliver stronger protection, better performance, and greater visibility without increasing operational complexity. To help organizations meet these demands, WatchGuard is introducing three new additions to its Network Security portfolio: Firebox T175, Prime Security Suite, and AP340 Wi‑Fi 7.

Turning Tool Sprawl into Coordinated Security

Your security tools see different parts of the story. But security decisions depend on the full picture. In this short video, learn how Universal Zero Trust Network Access (UZTNA) correlates signals from endpoint, identity, cloud, and network tools to identify risk, adapt access decisions, and help stop threats before they turn into compromises.

From audit season to always-on: what continuous network compliance looks like

Every network compliance calendar follows the same pattern: quiet between audits, then a spike of scrambling the week before the next one is due. During the quiet stretch, nobody actually knows whether firewall rules, segmentation, and access policies still hold as configured across the network. The audit does not create compliance. It samples it once, and then everyone moves on until the next one comes due.