Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Falcon Exposure Management Network Vulnerability Assessment: Demo Drill Down

CrowdStrike Falcon Exposure Management simplifies network security with its Network Vulnerability Assessment, offering a modern way to secure network infrastructure without complex legacy tools. Learn how the system utilizes your existing Falcon sensors to provide unmatched continuous visibility-instantly correlating new threats against your assets—and leverage authenticated scanning for deeper, more complete vulnerability inspection.
Build SOAR Workflows Instantly with Charlotte AI

With Charlotte AI and Falcon NextGen SIEM, build SOAR workflows instantly from natural language. Create reliable, intelligent automation that helps SOC teams respond at machine speed. CrowdStrike Falcon Next-Gen SIEM: Consolidate security operations with the world’s most complete AI-native SOC platform.

Fuel the Agentic SOC with High-Fidelity Data using Falcon Onum

Power your Agentic SOC with Falcon Onum. Watch how teams eliminate data bottlenecks and move at machine speed with intelligent pipeline management—collecting, enriching, and routing high-fidelity data across the enterprise in minutes. CrowdStrike Falcon Next-Gen SIEM: Consolidate security operations with the world’s most complete AI-native SOC platform. Subscribe and Stay Updated.

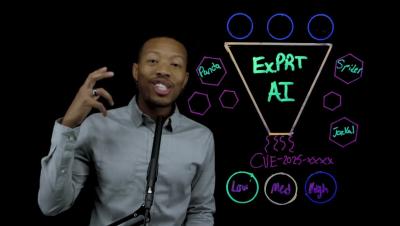
Under The Light: ExPRT.AI

n this episode of Under the Light, we take a closer look at ExPRT.AI—CrowdStrike’s approach to vulnerability prioritization that cuts through the noise. You’ll see how ExPRT.AI moves beyond static scoring models like CVSS, EPSS, and KEV by asking a better question: Will this vulnerability actually be exploited? We’ll break down: The three signals attackers rely on—and so does ExPRT.AI What makes a vulnerability worth their time A real-world story from Intermex that shows what this looks like in action And how all of it comes to life inside the Falcon platform.

Stop Living-off-the-Land Attacks with Falcon Endpoint Security: Demo Drill Down

Modern adversaries have shifted away from traditional malware toward weaponizing legitimate tools like RMM software, Windows utilities, and administrative programs. These "living-off-the-land" attacks blend seamlessly into normal business operations, making them extremely difficult to detect with traditional security tools.