Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why academic selfie fraud benchmarks fail in the real world

Academic deepfake datasets rarely static: generate an image, label it real or fake, done. Real-world fraud doesn't hold still. Zhaofeng Si, a PhD student at University at Buffalo and research scientist intern at Persona, breaks down the gap. Public academic datasets are mostly typical face swaps and diffusion-model-generated images with a fixed label. In the real world, there's an attack-and-defense loop. Fraudsters actively probe for ways to bypass detection, so defenses have to keep adapting instead of training against a static benchmark.
How to Remain Audit-Ready with Egnyte

Compliance regulations like CMMC, FINRA, and SEC don't pause, and neither should your audit readiness. Egnyte's Regulation-to-Audit framework is an end-to-end compliance solution that maps regulatory requirements directly to controls, artifacts, and audit-preparedness — keeping your organization compliant 24/7/365. Four powerful capabilities power this continuous compliance loop: · Sensitive Content Protection: Automatically scans, classifies, and labels regulated content across Egnyte and your connected repositories.

How Western Canada Lottery Corporation Is Modernizing 5,000 Retail Sites with Netskope SASE

Western Canada Lottery Corporation (WCLC) runs one of the world's most geographically dispersed retail networks: 5,000 lottery terminal locations across Manitoba, Saskatchewan, Alberta, and three northern territories. See how they replaced a fragmented multi-ISP setup with Netskope One SASE. In this 2-minute story, Adam Janssens, Director of Infrastructure and Operations, explains how WCLC: "The cost savings to move away from private connections to secure SD-WAN with Netskope is definitely multi-millions per year, which is a huge benefit to our organization and our provinces.".

Astra's Autonomous Pentest Against Other Tool

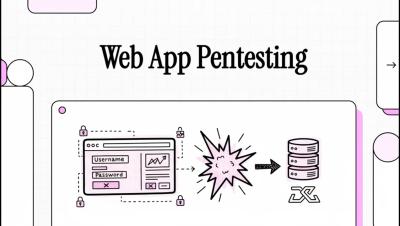
Astra vs. Other Tool: Who Finds More Real Vulnerabilities? How does Astra Autonomous Pentesting compare with the other tool when it comes to finding real-world vulnerabilities? In this independent benchmark, Astra was tested against the other tool to evaluate vulnerability coverage, depth, and true-positive findings. The results: 27 true-positive vulnerabilities identified 3.9× more vulnerability coverage 11 distinct vulnerability classes discovered Deep testing across business logic and application behaviour.

How to Create a Hyper-V Virtual Switch | External, Internal & Private Switches

Hyper-V Virtual Switches are essential for connecting virtual machines to networks and managing communication between Hyper-V VMs, the host, and external networks. In this video, learn about the different types of Hyper-V Virtual Switches and when to use each one: External Virtual Switch – Connects VMs to the physical network Internal Virtual Switch – Enables communication between VMs and the Hyper-V host Private Virtual Switch – Enables communication between VMs on the same host.

Introducing The GitGuardian Mixin Kit To Extend Docker Sandboxes for Safer AI Coding

Modern enterprise security is increasingly being tasked with keeping agents from affecting critical data and infrastructure. In this video, Dwayne, principal developer at GitGuardian, introduces how GitGuardian AI hooks extend the power of Docker Sandbox isolation. Their micoVM architecture plus the power of ggshield mean anyone can get an agent working in a secure way with very little effort. Chapters.