Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI in the MSSP SOC: From Pilots to Production

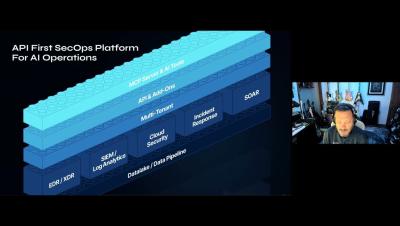
Every MSSP is under pressure to adopt AI, and most of the advice available is either vendor hype or generic guidance written for enterprise teams with one environment to manage. MSSPs face a harder problem: any AI they adopt has to work across dozens or hundreds of client stacks, respect tenant boundaries, and produce results an analyst can defend to a customer. In this session, Sr. Solutions Engineer Ken Westin lays out a practical roadmap for bringing AI into service provider security operations.

Intel Chat: Claude models reached real systems, an AI safety resignation & ShieldCrash [347]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

Intel Chat: OpenAI's Astra hits Critical, DEF CON phishing, Philippine nuclear breach [346]

Intel Chat with Matt Bromiley and Chris Luft. Stories covered: Chapters: The Cybersecurity Defenders Podcast — a podcast about cybersecurity and the people that keep the internet safe. New episodes drop weekly. Subscribe wherever you listen.

Ship a Working Detection Pipeline in One Workshop: Headless SOC with Grid by LimaCharlie

By the end of this hands-on workshop, you will have deployed a working detection pipeline, ingested a cloud log source, and shipped a bespoke dashboard app, all using Claude Code integrated with Grid by LimaCharlie. Along the way, you will see how Grid compresses the traditional SIEM/EDR/SOAR stack into a single automated workspace. We go well beyond standard EDR and SIEM use cases. What to expect.

Inside SECNAP: An Agentic MDR Platform Built on LimaCharlie

Joshua Strickland from SECNAP shows how his team built a full agentic MDR platform on top of LimaCharlie. SECNAP layers its own customer portal and SOC workflows directly on LimaCharlie's API, giving AI agents the same access to telemetry and response actions as a human analyst. Joshua will walk you through the customer portal, the SOC dashboard, and a live attack simulation on a sandboxed machine, including how AI agents handle tier one and tier two triage with Sonnet and Opus, and how a human analyst reviews and approves response actions before anything ships.


Ship a Working Detection Pipeline in One Workshop: Headless SOC with Grid by LimaCharlie

By the end of this hands-on workshop, you will have deployed a working detection pipeline, ingested a cloud log source, and shipped a bespoke dashboard app, all using Claude Code integrated with Grid by LimaCharlie. Along the way, you will see how Grid compresses the traditional SIEM/EDR/SOAR stack into a single automated workspace. We go well beyond standard EDR and SIEM use cases. What to expect.

Proving the value of security operations with Christopher Crowley [344]

Today we're speaking with Christopher Crowley, cybersecurity consultant through Montance and Senior Instructor with the SANS Institute, about the value of cybersecurity operations — how to measure it, how to express it to the business, and how AI is changing the work of the SOC.