Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Addressing Cyber Risk and the Rise of AI

In this episode of CISO Conversations: EU Data Regulations, Pierre-François Guglielmi, EMEA Field CISO at Rubrik, is joined by Trish McGill, an Executive Subject Matter Expert for Cyber Security IT/OT at De Heus Voeders and Nobian, Brian Wagner, Chief Technology Officer at Revenir, and Tim Clements, Owner of Purpose and Means. Together, they explore the impact of cyber-attacks and data regulations on business resilience, particularly concerning critical infrastructure, and how these factors ultimately affect profits.
GraphQL Security Breach: How 30 Million Accounts Were Hacked #hacked #databreach #graphql #api

In this video, we explore a real-world example of a GraphQL exploit that exposed 30 million user accounts to attackers. Learn how vulnerabilities in GraphQL led to access token generation and account takeovers, and what this means for API security.

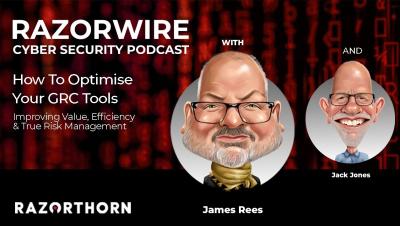
How to Optimise Your GRC Tools: Improving Value, Efficiency & True Risk Management

In this episode of Razorwire, we're joined by Jack Jones, creator of the FAIR risk model, to explore the complexities of Governance, Risk and Compliance (GRC) tools. We cut through the noise to deliver actionable insights on how to truly manage risk and improve the value and efficiency of your GRC solutions.