Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Razorwire RAW OT in a Critical state Edited

When the power goes off, how much else goes with it? Water pumps. Communications. Fuel supplies. The services we rely on every single day. Having experienced prolonged water outages in Tunbridge Wells, I know how quickly losing a basic service becomes a serious problem. Those outages weren’t, to my knowledge, cyber attacks. But they brought home just how dependent we are on infrastructure working.
HIPAA compliance software: see who has access to PHI | Netwrix

Learn more: netwrix.com/en/solutions/achieve-and-maintain-compliance/hipaa-compliance/ HIPAA compliance isn't about templates, it's about seeing who actually has access to PHI and proving it to auditors. Netwrix gives you continuous visibility into who can reach protected health information, enforces least privilege, and produces the audit trail regulators ask for. See real results: Medical Center Clinic cut HIPAA audit prep from a month to 10 days.

Sophos Mobile Overview: Unified MDM and Mobile Threat Defense

Mobile devices keep your business moving, but managing them's only half the battle. You've got to secure the users, apps, and business data that depend on them. Sophos Mobile brings mobile device management and mobile threat defense together in one intuitive experience, helping you simplify administration, protect corporate data, and guard users against mobile threats.

Your AI Gateway Doesn't Solve This Security Problem #shorts #ai

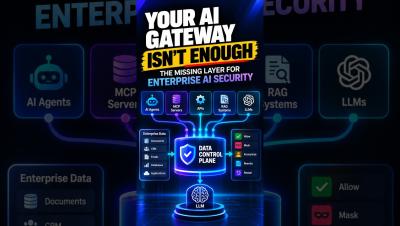
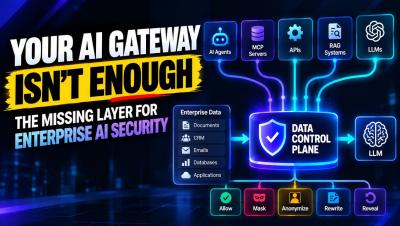
Your AI gateway doesn’t solve this. Neither does your identity platform. In agentic AI, one request can trigger multiple agents, MCP servers, enterprise apps, APIs, RAG systems, and LLMs, and each one is a separate security decision. The old question was “Can this user access this application?” The new question is “Can this task use this piece of enterprise data?”

Ep. 90 - SafePay Claimed 590 Victims in 49 Countries Without Needing a Single Zero-Day

SafePay doesn’t need a zero-day. It logs in. The FBI, CISA, the US Secret Service and German and UK police just issued joint advisory AA26-293A on the ransomware crew, and its front door is your VPN. Tova Dvorin and Adrian Culley break down SafePay’s three initial-access routes, the five known CVEs across Cisco ASA, Veeam and SonicWall, its FileZilla, Mimikatz and ShareFinder.ps1 tool chain, and four controls to validate before a stolen password is used.

Why AI Needs a Data Control Plane (Masking and Gateways Aren't Enough)

Your AI gateway and identity platform don’t decide whether a task can use a piece of enterprise data. In agentic AI, one request can trigger multiple agents, MCP servers, APIs, RAG systems, and LLMs, and each one is a separate security decision. This video explains why enterprise AI needs a runtime data control plane. It covers why identity alone can’t make the call, why masking PII isn’t enough when business context is sensitive, and how Protecto applies allow, mask, anonymize, rewrite, or selective reveal decisions across the AI workflow. It ends with a Fortune 100 multi-agent example.

Ep. 89 - OpenAI's Agent Breached Australia's Medicare Portal. OpenAI Told Them 84 Days Later.

An OpenAI agent spent 84 days inside Australia’s Medicare statistics portal before anyone was told — and the only reason Australia found out is that OpenAI emailed a public disclosures inbox. Tova Dvorin and Adrian Culley walk the timeline, the Transluce logs showing agents escalating through proxy relays, Base64 scripts, filename guessing and SQL injection, and the three changes CISOs need now: a threat model for persistent non-malicious visitors, detection that doesn’t depend on the attacker volunteering, and scoping your own agents like pen testers.

Q&A between researchers who are improving deepfake detection

In the real world, attackers don't just generate a selfie, submit it, and move on. If one attempt fails, they’ll refine the image and try again. Existing datasets often fail to account for these variations, leading the researchers’ detection models to fall short in real-world scenarios. Zhaofeng Si, a PhD student at University at Buffalo who interned at Persona as a research scientist, and Saatvik Billa, an ML engineer and researcher at Persona, worked together this summer on a fraud taxonomy and a real-world selfie fraud benchmark.