Cyber attacks are targeted at significant organizations, and this week is an excellent reminder that medical facilities aren't safe. Along with AT&T and Minneapolis Schools, three different medical establishments were hit and suffered from a loss of information in one way or another. Zoll, a Medical device and technologies company suffered staggering losses, while Cerebral gave up mental health information and Lawrence General Hospital lost HIPAA-protected information.
Cerebral is an online mental health company that's attempting to bring mental health care to patients around the country virtually. The company deals with tens of thousands of patients, and we've just learned that many of those patients may have had their information exposed to companies like Meta, Google, and TikTok. Cerebral is a startup company, and unfortunately, it isn't that unusual for startups to suffer from data issues such as this one.
HIPAA is a legal healthcare privacy standard passed into law by the Clinton administration. The law standardized how private healthcare information had to be protected and stored by hospitals. In its earliest years of inception, these rules were straightforward. Things have changed considerably. With the digitalization of healthcare records, it’s now easier than ever for patients and hospitals to access records, but it’s also easier for bad actors.
Nearly 93% of healthcare organizations experienced a data breach in the last three years, and most of these events could have been avoided with basic cybersecurity practices. To help healthcare entities mitigate cybersecurity risks and increase their data breach resilience, we’ve created a comprehensive healthcare cybersecurity guide optimized for the biggest security threats in the industry.
Earlier, even prior to the digitalization of healthcare records, it was still easier to keep the information secure and private. Records were in the physical form and could be protected in many ways. Now that people can pull up their entire health histories with the press of a few buttons, things are very different. With the information now being stored and processed online, the threat and risk exposures are equally high. So, to address such threats the U.S.
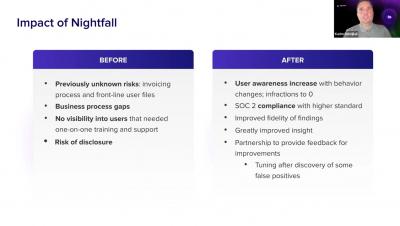
Last month, we hosted a webinar with our CISO, Karim Beldjilali, who was formerly the CISO of Rightway a healthcare startup. Karim shared important security lessons for healthcare organizations leveraging cloud applications across their workforce. We briefly share the highlights below.