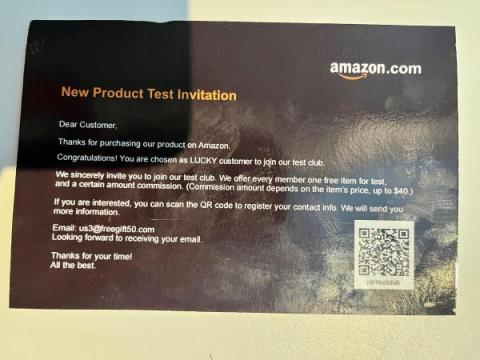
In the ever-evolving landscape of cyber threats, scammers and hackers are relentless in exploiting every avenue of communication. From emails to texts, calls to QR codes, malicious actors are finding new ways to compromise your privacy and security. One such emerging threat is the rise of QR code phishing attacks, a blend of QR codes and phishing designed to trick individuals into revealing sensitive information.
Now being commonly referred to as “Scama” – short for Scamming Method – these kits are being sold promoting highly advanced feature sets, turning the novice scammer into a pro. I’ve covered a number of Phishing-as-a-Service kits on this blog, but we’re seeing an evolution in both the kit features and how they’re being promoted on the dark web.
To celebrate National Computer Security Day, which is recognized on November 30 every year, KnowBe4 encourages all IT and security professionals to train their workforce how to stay safe from cybersecurity threats as the organization’s last line of defense. It is also crucial to focus on building a strong security culture by educating employees about today’s cyber threat landscape and how they can play a role in protecting the organization.
Once again companies are being warned to be wary of past employees who may turn rogue.
There’s been a “precipitous rise” in QR code phishing campaigns in 2023, according to Matthew Tyson at CSO. “For the attacker, QR codes bring a number of benefits, including some appreciated by legitimate businesses: they are easy to create and easy to use,” Tyson writes.
Phishing is a longstanding danger of the digital world that most people are aware of. Whether it happens via email, text message, social media, or any other means, phishing presents a risk to all users. In recent years, the growing popularity of QR codes for all manner of operations has created an environment ripe for cybercriminals to take advantage of.
With organizations heavily focusing on protecting the corporate endpoint, cybercriminals are switching focus onto mobile devices where users are more prone to fall for their social engineering tactics. We consume so much content from people you don’t personally know that it’s not part of your everyday process to stop and be critical of what’s being presented to you. And that’s exactly what cybercriminals are taking advantage of.
Huntress has released a report finding that business email compromise (BEC) attacks have risen in the third quarter of 2023. “64% of identity-focused incidents in Q3 2023 involved malicious forwarding or other malicious inbox rules, a key indicator of business email compromise (BEC),” the researchers write. “Another 24% of identity-focused incidents involved logins from unusual or suspicious locations.