Demo: Firebox Management in WatchGuard Cloud: Branch Office VPN (BOVPN)
Watch how to create a VPN between two Cloud-managed Fireboxes or third-party VPN point.


Prof. Avishai Wool, AlgoSec co-founder and CTO, breaks down the truths and myths about micro-segmentation and how organizations can better secure their network before their next cyberattack.
In our new threat briefing report, Forescout’s Vedere Labs describes how it analyzed files and tools used by an affiliate of the ALPHV ransomware group during an attack. ALPHV, also known as Black Cat, is a Ransomware-as-a-Service gang that was first discovered in November 2021.
Today’s threat landscape is evolving rapidly. Attackers are constantly adjusting their tactics and finding new ways to infiltrate organizations with increasingly sophisticated attacks to steal valuable data. As such, businesses and IT professionals must remain up to date on the industry’s latest threat intelligence in order to better understand the current state of this cybersecurity landscape and know their enemies to shore up defenses.
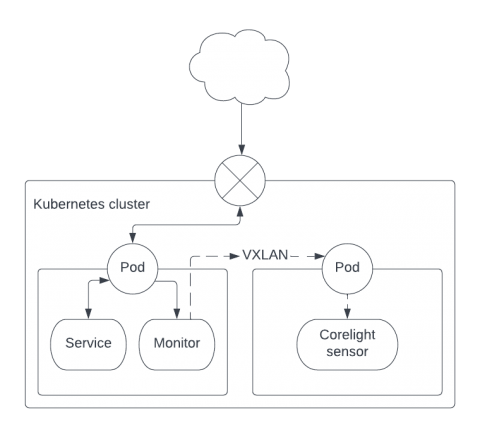
Monitoring container traffic and extracting rich security-centric metadata provides SOC analysts an inviolable source of truth for threat detection and incident investigation. This data complements the deep visibility provided by container agents and broad visibility through monitoring audit logs.