Protect your business, bounce back from disasters: learn the best practices for a reliable GitHub Restore and Disaster Recovery strategy that ensures business continuity.
This new feature automates assigning severity levels to each incident, allowing security teams to quickly identify the most critical ones and prioritize their response accordingly.
The ability to sign and verify the integrity and origin of software artifacts, such as Docker images, is critical to supply chain security. Let's try Sigstore, a new standard that promises to make this process much easier.
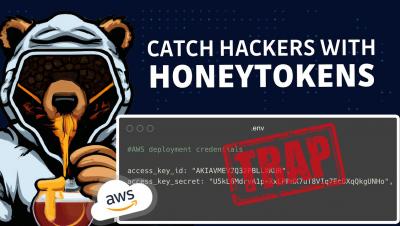
Misleading attackers to trigger alarms can stop them in their tracks and keep damage to a minimum. Honeytokens, like the ones you can make with GitGuardian's ggcanary, let you easily set such traps.
Read some of the highlights from CloudNativeSecurityCon 2023, the first-of-its-kind in-person event, grown from the conversations of the community on the front lines of open source security.