Security | Threat Detection | Cyberattacks | DevSecOps | Compliance
The Latest Cybersecurity News & Insights From Around The World
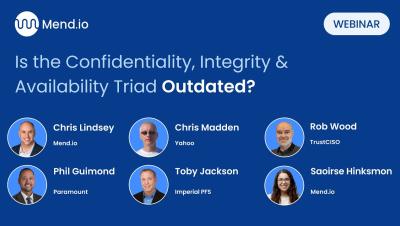
Security's Confidentiality, Integrity and Availability (CIA) Triad - Outdated or Still Relevant?
Are confidentiality, integrity, and availability still enough, or is it time to evolve our thinking? Join Chris Lindsey and a panel of tech leaders from leading enterprises, for a dynamic discussion on the relevance of the CIA Triad in modern security practices. Chapters: CIA Triad Basics and CVSS Scoring (0:00 - 0:55) Expanded Impact Metrics (0:55 - 2:02) Additional Impact Considerations (2:02 - 2:45) Historical Context and Evolution (3:01 - 3:41) Modern Challenges and Limitations (3:41 - 5:21) Risk-Based Prioritization (5:48 - 6:22) Business Communication Value (6:26 - 8:18)
Mend AppSec Platform Deep Dive
Watch Josh Newton demonstrate how the Mend AppSec Platform streamlines security across your codebase and software supply chain. Key Highlights: Intuitive Interface: Experience the ease of navigating the Mend AppSec Platform. Comprehensive Security Coverage: See how the platform addresses a wide range of security vulnerabilities. Seamless Integration: Discover how the platform seamlessly integrates into your existing development workflows. P.S.
Exploring Bug Bounty Programs and Pen Testing with Michael Vance from Navient
Kicking off your hacking journey? Bug bounty programs offer the perfect legal avenue to practice hacking without getting busted! Chapters.
What is code reachability?
Wait – what is code reachability Let's go back to basics with Amit Chita about decluttering your digital closet in a series of short videos about a subject that's too often overlooked.
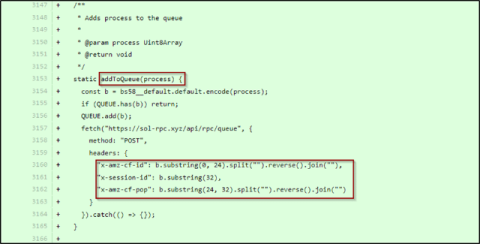
The @Solana/web3.js Incident: Another Wake-Up Call for Supply Chain Security
On December 2, 2024, the Solana community faced a significant security incident involving the @solana/web3.js npm package, a critical library for developers building on the Solana blockchain with over 450K weekly downloads. This blog post aims to break down the attack flow, explore how it happened, and discuss the importance of supply chain security.
Automatic dependency updates have never been easier
Implementing Mend Renovate Enterprise has never been easier: 24/7 support, dedicated team guidance, and additional features for increased productivity. Book a time with a product specialist to learn more.
CTO vs VP R&D
Implementing Mend Renovate Enterprise has never been easier: 24/7 support, dedicated team guidance, and additional features for increased productivity.
Benefits of VEX for SBOMs
As Software Bill of Materials (SBOMs), become increasingly necessary and in some cases, required by private companies and governments globally, they are meant to provide transparency and help organizations understand what is in their software. But if SBOMs are so helpful, how come nobody knows what to do with them?
Mend.io is a Strong Performer in the Forrester Wave Software Composition Analysis, Q4 2024
It should be no surprise that the world runs on open source software. According to the latest Forrester Wave Software Composition Analysis Q4 2024 report an “astonishing 77% of codebases are comprised of open-source software.” Since a “considerable amount of an application’s risk is due to third-party sources,” software composition analysis (SCA) tools remain the lifeblood for securing modern applications and bringing greater transparency to the software supply chain.