Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Vulnerability Management Benchmarking: Metrics and Practices of Highly Effective Organizations

This webinar dives deep into vulnerability management metrics, the challenges of maintaining cloud and ephemeral assets, and the discrepancies in vulnerability management across different organizations. Join us as we unravel the nuances of MTTR (Mean Time to Remediate), SLA (Service Level Agreements), and how high-performing organizations manage cybersecurity threats more efficiently. Don't miss this discussions on the role of data democratization in cybersecurity and how organizations can transition from reactive to proactive vulnerability management, no mature your VM maturity.

Nucleus

Nucleus is a Risk Based Vulnerability Management (RBVM) solution that automates vulnerability management processes and workflows, enabling organizations to mitigate vulnerabilities 10 times faster.

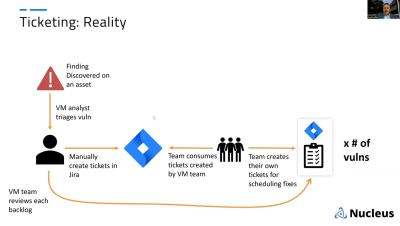
What Does a Solid VM Ticketing Workflow Actually Look Like?

In this webinar, Scott Kuffer discusses the challenges and best practices of vulnerability management workflows and ticketing. He emphasizes the discrepancy between vulnerability management teams' priorities and the priorities of the business as a whole. Scott explores different ticketing workflows, starting with basic vulnerability-based tickets and progressing to more advanced options such as asset-based, team-based, and action-based tickets. He highlights the benefits of automating ticket creation and reporting, as well as the potential for redefining how vulnerability management is approached within organizations.


How Nucleus Security Streamlines Vulnerability Management for Government Agencies

Nucleus Security is proud to announce its recent achievement of Federal Risk and Authorization Management Program (FedRAMP®) authorization at impact level Moderate, making it the go-to choice for government agencies seeking top-tier vulnerability management solutions.

Visualizing Vulnerability Management: What Does a Single Pane of Glass Really Look Like?

Single Pane of Glass (SPOG) is a common buzzword that sends shivers down the spines of technical folks everywhere. Yet, executive teams ask for it, especially in vulnerability management. At the same time, the complex and fragmented nature of modern IT environments wreaks havoc on organizations aiming to understand their current location related to remediating and patching risks. So, what exactly is a single pane of glass, and what does it look like for enterprises today?

National Cyber Security Centre (NCSC) Vulnerability Management Guidance Checklist

As of February 12, 2024, the National Cyber Security Centre (NCSC) has released Version 2.0 of its vulnerability management guidance. This update provides organizations with the latest strategies and practices to identify, assess, and manage cybersecurity vulnerabilities effectively. The NCSC’s updated guidance on vulnerability management outlines the importance of proactively managing vulnerabilities to secure technical estates.

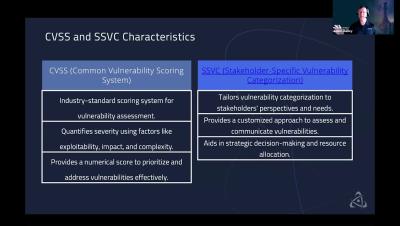
Applying Vulnerability Intelligence to CVSS and SSVC Frameworks

In this presentation, we explore the intersection of vulnerability intelligence and prioritization frameworks such as CVSS and SSVC as a means for strategically and rapidly prioritizing vulnerabilities to stay ahead of exploitation risks. We delve into the process of applying real-time threat intelligence tailored to the vulnerability landscape to enhance decision-making, optimize resource allocation, and ensure a precise and proactive defense against cyber threats.

Nucleus Security Raises $43 Million Series B Funding to Lead Innovation in Enterprise Risk-Based Vulnerability Management

Nucleus Security announces it has secured $43 million in Series B funding led by Arthur Ventures and Lead Edge Capital. This milestone marks a significant leap forward in the company's mission to redefine how enterprises manage risk exposure from vulnerabilities across infrastructure, cloud, and application portfolios in one unified platform.