Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Snyk's shift left approach to API development

Snyk’s developer security platform provides developers and security professionals with the tools they need to build and operate modern applications securely. Snyk enables users to shift security left and to embrace a DevSecOps model. Modern application development teams understand that shifting left means bringing information to developers’ fingertips as early as possible in the development process to create efficient and secure applications and development processes.
CASB Solution

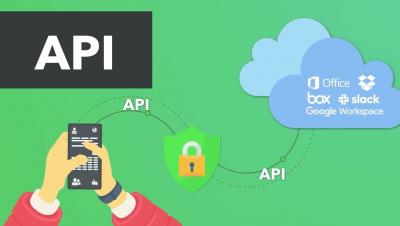
A cloud access security broker (CASB), is cloud-delivered software or on-premises software and/or hardware that acts as an intermediary between users and cloud service providers. The ability of CASBs to address gaps in security extends across software-as-a-service (SaaS), platform-as-a-service (PaaS), and infrastructure-as-a-service (IaaS) environments. In addition to providing visibility, a CASB also allows organizations to extend the reach of security policies from their existing on-premises infrastructure to the cloud and create new policies for cloud-specific contexts.

Interview with a Hacker How are Attackers Targeting Mobile Devices

Every organization today utilizes mobile as a productivity tool by providing a full range of access to corporate resources for iOS and Android devices. With employees accessing O365, G Suite, Salesforce, and other services where attackers see an opportunity. Join Lookout and Eurofins to learn from the hacker's perspective.

Critical Capabilities for Mobile Vulnerability Management

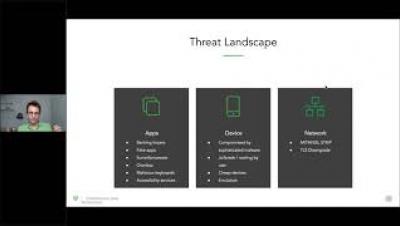
As organizations enable employees to work remotely, mobile devices and wireless networks will be key tools for maintaining communication and remaining productive. Allowing employees to work productively from any device and any location can open users to the risks that come with the shared nature of a mobile device. When your employees work from a personal device with access to corporate data, the device's health must be taken into account. It must be assessed for compliance with corporate security and risk policies.

Five worthy reads: Into the metaverse

Five worthy reads is a regular column on five noteworthy items we’ve discovered while researching trending and timeless topics. This week we will explore the concept of the metaverse and what it holds for the future of technology and user experience. Illustration by Dorathe Victor When Facebook changed its name to Meta in September 2021, a new buzzword took over the tech world: the metaverse.

Elevate AWS threat detection with Stratus Red Team

A core challenge for threat detection engineering is reproducing common attacker behavior. Several open source and commercial projects exist for traditional endpoint and on-premise security, but there is a clear need for a cloud-native tool built with cloud providers and infrastructure in mind. To meet this growing demand, we’re happy to announce Stratus Red Team, an open source project created to emulate common attack techniques directly in your cloud environment.