Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Delivering Intelligent IT Foundations for Safe AI Usage

JumpCloud CTO Greg Keller explains why traditional, fragmented IT tools create a critical Zero Trust gap for AI agents, bots, and non-human identities (NHIs). The biggest inhibitor to innovation isn't restrictive policy—it's the internal lack of a unified identity foundation. Learn how to address "identity sprawl" and transform IT operations to deliver auditable trust, extend Zero Trust enforcement to machine-to-machine interactions, and build the Intelligent IT foundations required for safe, accelerated AI adoption.
SOAR in the AI era: How SAP uses intelligent workflows to build an AI SOC

SOAR was created to help security teams work faster and more consistently by automating and orchestrating core security operations. It has always had to adapt to new and evolving technologies, but our current AI era has brought about a turning point. As cloud environments scale, manual playbooks can’t keep up. Now, it’s not enough to automate. We need systems that can understand the context they’re running in and adapt accordingly.

The New AppSec Reality: AI Anxiety, Silent Flaws, and Supply Chains

We recently published a series of polls across our social channels to get a pulse on some of today’s application security concerns with AI. These recent conversations with our community reveal a clear and urgent shift in the application security landscape. Results show that while established challenges like software supply chain security remain top of mind, the rapid pace of AI has created a new center of gravity for anxiety.

Prompt Injection Attacks in LLMs: Complete Guide for 2026

In February 2023, a Stanford University student conducted a study that turned into one of the most widely followed security tests in AI history. Kevin Liu performed a simple prompt-injection attack, tricking Microsoft Bing Chat into disclosing its internal codename, Sydney, and exposing the entire list of its system prompts. The attack utilized no high-end toolkit, no zero-day, and no privileges, only specially crafted natural language.

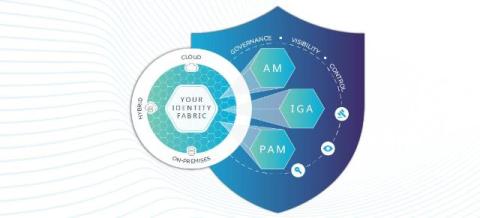
AI in IAM: How much value is it really providing?

Let’s face it, AI is everywhere now. It has moved from novelty to necessity, reshaping the way we work, make decisions and secure our organizations. It guides how we plan trips, shop for essentials and discover information – but one of its most profound impacts is happening across enterprise environments.

Best Practices for Implementing Data Tokenization

Data is no longer confined to a few clean relational systems. It now flows through microservices, data lakes, event streams, vector databases, and LLM pipelines. Sensitive information spreads quickly, and once it reaches ungoverned surfaces—logs, analytics exports, embeddings—it becomes extremely painful to unwind. Tokenization is one of the few controls that can both minimize data exposure and preserve business functionality.

The Mythical 1+1=3 Model in Cybersecurity

The mythical 1+1=3 model in security? It happens when the tools you already own stop working in isolation — and start working as a system. Jay Wilson and Garrett Hamilton dig into why Reach’s platform approach matters: not just enhancing individual controls, but creating compounding value across identity, endpoint, email, and network. When visibility, configuration, and enforcement align, the outcome isn’t incremental — it’s exponential.

APIs are the Language of AI. Protecting them is Critical.

APIs are the Language of AI. Protecting them is Critical. In this discussion, A10 Networks security experts Jamison Utter and Carlo Alpuerto explore the emerging impact of Agentic AI on the API security landscape. They delve into how AI agents, as new API consumers, are driving an explosion in endpoints and exacerbating existing security issues, pushing API protection higher up the security practitioners' priority list.