Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why AI Privacy is a Competitive Advantage (Not Just Compliance)

In most startups building or using AI, privacy often gets treated like a checkbox that legal or security will “handle later.” That mindset quietly kills deals, scares off enterprise buyers, and limits your access to the very data your models need. Here is the truth that more founders and CTOs are embracing. Privacy makes your product easier to buy, models better to train, and business more valuable.
Charlotte AI - 2025 MITRE ATT&CK Enterprise Evaluations

The 2025 MITRE ATT&CK Enterprise Evaluations featured sophisticated cross-domain attacks from Scattered Spider, and CrowdStrike's Charlotte AI proved essential in delivering 100% detection and protection with zero false positives. Charlotte AI accelerated every stage of security operations with Agentic Detection Triage for instant verdicts, Agentic Response that investigates alerts like expert analysts, and command-line analysis in plain language.

Mitigating Credential Phishing in the Age of AI and Cloud Convergence

Phishing remains one of the most effective methods for stealing credentials and breaching enterprise environments. Despite advanced email and browser protections, attackers now leverage AI, and automation to outpace traditional defenses. The Verizon 2024 Data Breach Investigations Report found that 68% of breaches involve the human element, often triggered within seconds of a phishing lure, just 21 seconds to click and 28 seconds to submit credentials.

AI, Creators & Agentic Commerce - A Conversation with Cloudflare CSO Stephanie Cohen

In this episode of This Week in NET, host João Tomé sits down with Stephanie Cohen, Cloudflare’s Chief Strategy Officer, for a candid conversation about AI, content creators, financial services, partnerships, and the future of the Internet. Stephanie shares how Cloudflare is helping keep the Internet open and resilient — from giving creators transparency and control over AI scraping, to enabling new models of agentic commerce through partnerships with Visa and Mastercard, to empowering organizations of all sizes through Cloudflare’s global network.

The OWASP Top 10 for Agentic Applications: A Milestone for the Future of AI Security

The OWASP GenAI Security Project has officially released its Top 10 for Agentic Applications, the first industry-standard framework focused on the operational risks created by autonomous and semi-autonomous AI systems. AI has evolved in a way that directly changes how enterprises need to think about security. We started with machine learning systems designed to classify and predict.

OWASP Top 10 for Agentic Applications (2026): What Developers and Security Teams Need to Know

Agentic AI is moving into production in CI/CD pipelines, internal copilots, customer support workflows, and infrastructure automation. These systems no longer just call a model. They plan, decide, delegate, and take actions on behalf of users and other systems. This creates new attack surfaces that do not map cleanly to traditional application security or even the OWASP Top 10 2025.

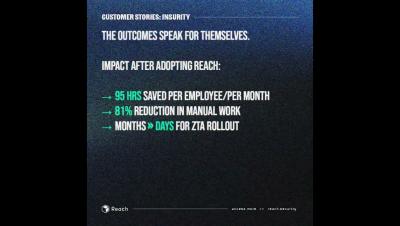
How Insurity Cut Manual Security Work by 81%

95 hours back. Every. Single. Month. One of the many outcomes from our ZTA journey with Insurity. They didn’t just deploy Zero Trust — they operationalized it. Reach unified controls, automated remediation, and eliminated the manual effort slowing progress. Results:︎ 81% less manual work︎ 95 hours saved per employee per month︎ Months → days for rollout︎ Zero Trust that sticks.

When Al Agents go Rogue: What you're Missing in your MCP Security

No Fluff, Just Real-World Threats This isn’t your typical marketing webinar. We cover what Agentic AI actually looks like in production, how MCP servers work to broker instructions, and what kind of new threats are emerging. Agentic AI isn’t coming. It’s already here. Autonomous agents are now operating in production environments, reasoning, remembering, and taking real actions across your systems. They’re not just generating content. They’re triggering workflows, modifying records, and making decisions. And they’re doing it over APIs.

Securing AI Agents: How to See MCP Servers and A2A Traffic with Salt Security

AI agents have moved past conversation into action. They book transactions, pull sensitive data, and chain tools together through the Model Context Protocol (MCP) and Agent-to-Agent (A2A) traffic. Every one of those actions runs on APIs, and that connective tissue is where the risk sits. Salt Security Co-Founder and CEO Roey Eliyahu and VP of Product Strategy Nick Rago walk through the risks in the agentic action layer and show what Salt does about them.

You Can't Have AI Security Without API Security: The Agentic Action Layer

AI agents run on APIs, and that is where most security programs have a gap. Salt Security Co-Founder and COO Michael Nicosia and CMO Michael Callahan explain why you cannot secure AI without securing the APIs underneath it. An AI agent uses an LLM to reason and an MCP server to broker calls out to other systems, and every one of those calls is an API interaction. Deploy one agent and the traffic multiplies. Deploy hundreds, and the internal east-west traffic climbs to several times what a pre-AI environment carried.