Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Protecting PHI Beyond Names and ID Numbers

A few years ago, an Australian government health agency released what it believed was a fully de-identified dataset covering 10% of the national population. Names, addresses, and other obvious identifiers had been stripped out. Researchers showed individuals could be re-identified using nothing more than rare medical procedure codes and treatment dates cross-referenced with publicly available information. No names were needed.
Is the SaaS Market Is About to Collapse?

AI coding is disrupting the SaaS market. GRC tools, CRM products and enterprise dashboards that cost hundreds of thousands can now be built internally in weeks using Codex and other AI models. SaaS companies know this is happening, which is why they're locking customers into three to five year contracts. But there's a serious security risk nobody is talking about. If you're vibe coding internal tools and applications, you need continuous security testing to catch vulnerabilities before attackers do. The faster you develop, the faster you need to detect breaches.

The Agentic Attack Surface Is Growing Faster Than Your API Inventory. Here's How to Catch Up

Ask any security leader how many APIs their organization runs, and you’ll usually get a confident number. Ask them how many of those APIs are actually being called by an AI agent, a copilot, or an automated workflow right now, and the confidence tends to disappear. That gap is the problem. APIs have always outpaced the inventories built to track them; new services ship every sprint, integrations get added without a ticket, and old endpoints get deprecated without ever being switched off.

How we brought agentic workflows to Cloud SIEM with the Datadog MCP Server

Security engineers using Cloud SIEM spend their day-to-day investigating signals, tuning detection rules, managing suppressions, running historical jobs across interconnected workflows, and more. Agents are becoming a practical way to navigate that complexity, and we built a set of security tools for the Datadog MCP Server to support them. Cloud SIEM is only one part of a broader cloud security ecosystem, so the Security MCP toolset has to grow across many teams and products.

Agent verification might just be KYC/KYB

Every time a card gets issued or a payment moves, something has to decide, in milliseconds, whether it's legitimate. That's the problem Robin Gandhi, chief product officer at Lithic, solves every day. Lithic builds the programmable infrastructure behind modern card issuing and money movement for developers, digital banks, and financial institutions.

AI in risk management: Practical applications and considerations

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Benchmarking 13 AI models on rediscovering known CVEs

TL;DR Every frontier model launch now comes with the same cybersecurity claim: it finds vulnerabilities. But does it work on a real bug in a real repository, or just on a curated example? Of the dozen models you could pick, which is worth trusting with code review? And since the strongest models cost ten times or more per run than the cheapest, what does that extra spend actually buy you in bugs found?

A Guide to Firewall Management: How to Set Up Proper Firewall Rules

Firewalls remain one of the most foundational controls in any security program. Nearly every organization has at least one, and in many cases, hundreds. Despite widespread deployment, firewalls are frequently a source of unintended exposure rather than protection. The reason is almost always in how firewall rules are maintained over time, not the technology itself.

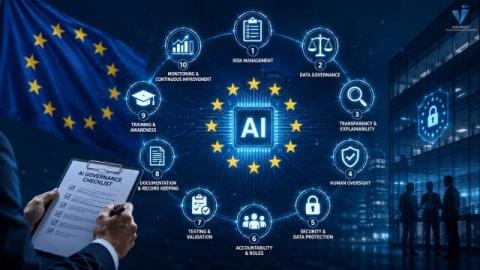
EU AI Act Readiness: 10 Controls Every Organization Should Implement in 2026

This is for compliance and security leaders who already know the EU AI Act applies to them and need a concrete control set for where the law actually stands today — not a summary written before the rules changed. Awareness is done; 2026 is the year of implementation, and the rules just moved. On 29 June 2026 the Council of the EU gave its final green light to the Digital Omnibus on AI — the package that resets several of the dates compliance teams have been building toward.