Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Security Trifecta: Operationalizing API Protection with AWS, Wallarm, and Coralogix

In the modern digital world, API’s are no longer just “connectors” – they are the real security product. Whether you are a Fintech processing payments, a SaaS platform managing multi-tenant data, or an E-Commerce giant handling the bulk of sales, your API’s are the foundation of your customer registration, checkout experiences, and partner ecosystems. However, that transition has made API’s the fastest-growing attack surface in history.
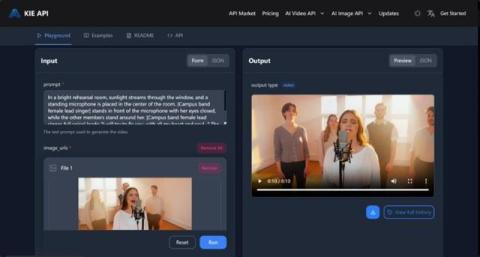
Kling Video 2.6 API: How to Build Automated Visual Simulation Workflows

The landscape of generative media has shifted from simple prompt-based experimentation to sophisticated, integrated production pipelines. With the release of Kling 2.6, the focus has moved toward "Native Audio-Visual Generation"-a breakthrough that allows developers to synchronize high-fidelity visuals with context-aware sound in a single automated step. For platforms focusing on digital senses and technical security, the Kling Video 2.6 API offers a robust framework for building simulations that were previously too resource-intensive to automate.

6 Lessons Security Leaders Must Learn About AI and APIs

Most organizations treating AI security as a model problem are defending the wrong layer. Security teams filter prompts, patch jailbreaks, and tune model behavior, which is all necessary work, while the actual attack surface sits largely unexamined underneath. That surface is the API layer: the endpoints AI systems use to retrieve data, call tools, and take action on behalf of users. This isn't a theoretical gap.

You're Not Watching MCPs. Anthropic's Vulnerability Shows Why You Should Be.

Last week, researchers at OX Security published findings that should stop every security leader in their tracks. They discovered a critical vulnerability baked directly into Anthropic's Model Context Protocol SDK, affecting every supported language: Python, TypeScript, Java, and Rust. The result: remote code execution on any system running a vulnerable MCP implementation, with direct access to sensitive user data, internal databases, API keys, and chat histories. Over 7,000 publicly accessible servers.

Attacking the MCP Trust Boundary

Every secure API draws a line between code and data. HTTP separates headers from bodies. SQL has prepared statements. Even email distinguishes the envelope from the message. The Model Context Protocol (MCP), the fast-growing standard for connecting AI agents to external services, inherits that gap from the models it sits on top of.

The Governance Gap: How the EU AI Act Makes API Security a Compliance Imperative

Your legal team just handed you a 400-page document and said "figure out compliance." The EU AI Act is live, your organization falls under its scope, which is broader than many expect. Even non‑EU companies must comply if their AI systems are used, deployed, or produce effects within the European Union. In practice, that means that global organizations building or integrating AI models cannot treat the Act as a regional regulation.

Why API Discovery Is the First Step to Securing AI

AI risk doesn’t live in the model. It lives in the APIs behind it. Every AI interaction triggers a chain of API calls across your environment. Many of those APIs aren’t documented or tracked. That’s your real exposure. Shadow API discovery gives you visibility into those hidden endpoints, so you can find them before attackers do. If you don’t know which APIs your AI relies on, you can’t secure the system.

Claude Mythos Changed Everything. Your APIs Are the First Target.

Anthropic just released Claude Mythos Preview. They did not make it publicly available. That decision alone should tell you everything you need to know about what this model can do. During internal testing, Mythos autonomously discovered and exploited zero-day vulnerabilities across every major operating system and web browser. It found a 27-year-old bug in OpenBSD. A 16-year-old vulnerability in a widely used media codec.

Everyone Is Securing the Wrong Layer of AI

The AI security market is crowded. Vendors are racing to protect prompts, harden models, detect jailbreaks, and scan for data leakage at the LLM layer. The investment is real. The intent is good. And most of it is missing the point. Here is the problem: agents do not just think. They act. They call APIs. They trigger workflows. They write to databases, send emails, move money, and modify production systems.

The AI Supply Chain is Actually an API Supply Chain: Lessons from the LiteLLM Breach

The recent supply chain attack involving Mercor and the LiteLLM vulnerability serves as a massive wake-up call for enterprise security teams. While the security industry has spent the last year fixating on prompt injections and model jailbreaks, this breach highlights a far more systemic vulnerability. The weakest link in enterprise AI is not necessarily the model itself. It is the middleware connecting the models to your data.

The Era of Agentic Security is Here: Key Findings from the 1H 2026 State of AI and API Security Report

The era of human-centric API consumption is officially ending. Over the past year, enterprises have rapidly transitioned from simply experimenting with Generative AI to deploying autonomous AI agents that drive core business operations. These agents act as digital employees. They utilize Large Language Models (LLMs) for reasoning, Model Context Protocol (MCP) servers for connectivity, and internal APIs for execution. This evolution has fundamentally altered the enterprise attack surface.

Building Smarter Virtual Assistants with Gemini 3 Flash API: AI for Seamless Workflow Automation

As teams become more distributed and workloads continue to increase, the need for effective automation tools has never been greater. Traditional methods of collaboration often fall short when it comes to handling repetitive tasks, managing high volumes of information, or providing real-time, intelligent support. That's where AI virtual assistants come in, changing how teams collaborate, streamline workflows, and boost productivity.

Everyone is Deploying AI Agents. Almost Nobody Knows What They're Doing

AI agents are operating inside your enterprise; querying databases, triggering workflows, and taking action through APIs. As AI agents are adopted, organizations cannot see, track, or control what these agents are actually doing. In this session, Roey Eliyahu, Co-Founder and CEO of Salt Security, challenges the industry’s narrow focus on LLM safety and exposes the much larger, invisible attack surface created by agentic systems.

Codex API In DevSecOps: Balancing Developer Speed With Secure Code Review

AI-assisted coding is no longer a side experiment. It is becoming part of daily engineering workflows, from drafting functions and refactoring legacy code to generating tests and accelerating routine implementation work. That shift is why the Codex API now belongs in a broader DevSecOps conversation, not just a developer productivity discussion.

The Agentic Stack Explained: How LLMs, MCP Servers, and APIs Work Together

The term AI agent is dominant in current cybersecurity discourse. Vendors, analysts, and CISOs all use the label, yet technical confusion remains regarding how agents actually operate and where the security risks reside. Beneath the surface-level familiarity, there is often significant confusion about what an AI agent actually is, how it operates technically, and most importantly for security teams, where the risk actually lives.

How does Sisense stay on top of API Attacks?

Sisense powers analytics experiences inside the applications businesses rely on every day. As an API-first platform, securing those connections is critical, especially as AI agents increasingly operate through APIs to access data and trigger workflows. In this conversation, Sangram, CISO and VP of IT at Sisense, and Michael Callahan, CMO at Salt Security, discuss how Sisense approached API security strategically to protect their platform, maintain customer trust, and support innovation in the Agentic AI era.

Open Banking API Security: The Complete Guide for 2026

Global Open banking API call volumes are set to cross the 720 billion mark by 2029, and attackers know it. With the global open banking market surging past $38 billion in 2025 itself and projected to exceed $115 billion by 2030, the financial data flowing through these APIs is highly lucrative for threat actors. With over 7.5 million calls made to just AI APIs, they have now graduated from a technical challenge to a business imperative.