Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The AI notetaker you can't see in the participant list

For about three years, the governance question around AI meeting assistants had a convenient property: you could see them. The tool joined the call as a named participant. It appeared in the attendee list. Everyone in the meeting had at least the theoretical opportunity to object, and a security team reviewing an incident could reconstruct which meetings had been recorded by looking at who else was in them.
Many New Technologies, Products, and Tools for Modern Protection Programs in New York, New Jersey, and Florida

A lot of buyers still start with the most visible layer of protection: cameras, guards, or a front desk presence. The real gap usually sits behind that first impression. If doors, credentials, visitor flow, and response routines are loose, the rest of the program ends up documenting problems instead of preventing them.

Why Modern Email Security Requires More Than Sender Reputation

For years, email filtering worked from a stable premise: malicious messages would expose themselves through something observable. A suspicious domain, a spoofed sender, a known-bad attachment or a URL with poor reputation gave defenders a concrete signal to block. Those controls still stop commodity phishing. What has changed is that many convincing attacks now inherit trust rather than imitate it.

4 Simple Habits To Stop Email Hackers

Stopping email hackers requires adopting four specific habits: letting AI filter inbound messages, identifying manufactured urgency, verifying requests through second channels, and locking accounts with passkeys. These zero-skill routines block the credential-harvesting tactics that compromise shopping, streaming, and financial profiles. Consider a content creator receiving a brand partnership offer from a recognizable sportswear company. The logo perfectly matches the corporate website, the tone sounds professional, and the message includes a simple link labeled to review the contract.

4 Easy Standards To Protect Team Data

Protecting team data starts at the workstation level, moving beyond access logs or password policies to secure the physical environment each employee operates in every day. Inconsistency creates immediate exposure points across the office because varying screen habits and device positions generate discrete gaps that software policies cannot close alone.

4 Easy Steps To Secure Mobile Field Work

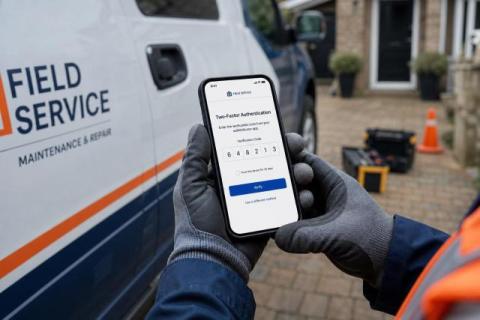
A field tech at a customer site can log into a scheduling app, pull up an invoice, and snap a site photo in under five minutes while connected to open Wi-Fi. That mobile device holds customer addresses, signed work orders, access codes, account credentials, and job-site photos. Unlike an office workstation that sits behind a firewall and never leaves the building, a field device moves through unfamiliar networks and high-risk physical spaces daily.

Is an AI SOC Better Than MDR? What Security Teams Should Weigh

Security teams are expected to investigate more alerts than they have people to handle. IBM's 2025 Cost of a Data Breach Report puts a number on what that gap costs: organizations take an average of 158 days to identify a breach, and a further 83 days to contain it. That is 241 days of exposure, the fastest pace in nine years, and still measured in months. For most SOC teams, the bottleneck was never finding threats. It was having enough people to do anything about them.

Software for Non-Profits Canada: Top 5 Platforms to Scale Your Mission

Operating a registered charity or non-profit organization in Canada involves navigating complex daily workflows, maintaining accurate record-keeping, and adhering to Canada Revenue Agency regulatory compliance. Beyond meeting administrative standard procedures, teams must coordinate volunteer management, manage communications, and maintain complete operational oversight to build long-term donor accountability. Choosing the right digital platform plays a central role in driving staff efficiency, optimizing response times, and maximizing overall customer satisfaction.

6 Administrative Tasks Every Personal Injury Law Firm Can Automate With AI in 2026

Personal injury law firms spend a significant amount of time on administrative work that supports-but does not replace-legal expertise. Reviewing medical records, preparing demand letters, drafting litigation documents, organizing case files, summarizing evidence, and communicating with clients are all essential parts of managing a case, yet they can consume valuable hours every week.

Your Scanners See a Different Internet Than Your Users Do

A few years ago, cloaking was mostly a black hat SEO problem. Someone would serve one version of a page to Googlebot and another to human visitors, and the worst outcome was a spammy search result. It has since become one of the more effective evasion techniques in the phishing and malvertising toolkit, and most security teams are still measuring their external exposure from a vantage point that attackers stopped caring about some time ago.