Built on real outage data, the new interactive tool enables enterprises to quantify hidden downtime losses and benchmark their cyber resilience in minutes.
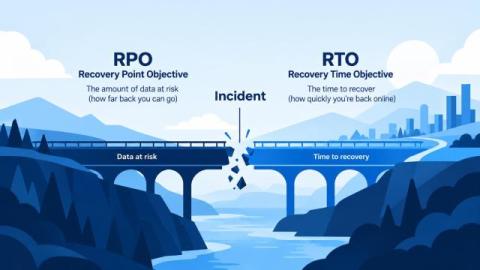
Recovery time objective (RTO) is how long a system can be down before the impact becomes unacceptable. Recovery point objective (RPO) is how much data the business can afford to lose, measured as a window of time before the incident. RTO looks forward from the moment things break. RPO looks backward from it. That distinction takes a paragraph to explain and years to get right, because the difficult part was never the definition.
Two hours of downtime is all it takes to plunge nearly 1 in 5 automakers into an immediate crisis, while 87% cannot sustain an outage beyond 24 hours. With 78.5% of companies running unsegregated IT/OT networks and 5 in 9 of plant managers unprepared for ransomware, a single cyber incident now threatens rapid assembly line paralysis across the supply chain.
A field tech at a customer site can log into a scheduling app, pull up an invoice, and snap a site photo in under five minutes while connected to open Wi-Fi. That mobile device holds customer addresses, signed work orders, access codes, account credentials, and job-site photos. Unlike an office workstation that sits behind a firewall and never leaves the building, a field device moves through unfamiliar networks and high-risk physical spaces daily.
When a cyber incident hits, your team's technical skills are definitely put to the test. But beyond the digital forensics and system recovery, another skill's just as important for getting through it: communication. Good communication is the backbone of any successful incident response (IR) strategy, but people often don't think about it until it's too late. This guide will show you how to build a clear communication framework for your IR team.
A few years ago, I was sitting across from a security leader at a large enterprise. They had just deployed their first wave of AI agents. When I asked how they were thinking about the security of it, they paused for a moment and then said something I haven’t forgotten. I felt that. Not just as a researcher, but as someone who had been in enough of those rooms to know it was not one person’s gap. It was the whole industry’s gap.
Observability is not the problem anymore. The data that tells you a change will break something usually already exists. Most teams have the events, the logs, the configuration history. What is missing is the step that turns all of it into a clear yes or no on a specific change, while there is still time to pull it. Garrett Hamilton, CEO of Reach Security, on objective data and the changes that get made before anyone checks.
Things like storms, hacking attempts, blackouts, broken machines, or connection problems might break essential systems. If messages can't get through, companies struggle to run smoothly, keep data safe, or stay on track. In those moments, clear and protected contact matters more - mistakes creep in when people aren't sure what's happening. Being ready ahead of time helps teams keep talking, working, and supporting others - even when surprises hit.
In this short video, Gary Perkins, explains why having an incident response retainer in place before an attack can make the difference between a minor disruption and a major business impact. The faster the response, the better the outcome.
Security incidents are rising with each passing year. The global cost of cybersecurity incidents was $10.5 trillion at the end of 2025. It is projected that data breaches will increase by 40% in 2026, as reported in SentinelOne. Security incidents are no longer isolated events. Many organizations use security systems such as SIEMs, EDRs, and identity telemetry, which generate alerts based on detection logic. While some controls can block the activity, others may allow it to continue undetected.