Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

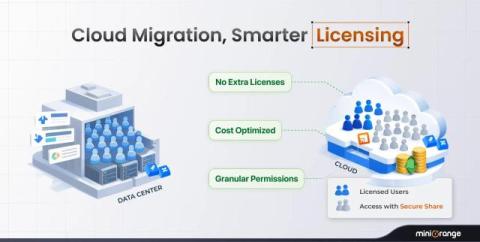
How Secure Share for Jira & Confluence Simplifies Atlassian Migration

Migrating from Atlassian Data Center (DC) to Cloud is a strategic move for many organizations. While migration brings scalability, flexibility, and cost benefits, it also introduces challenges, especially around secure external access, data sharing, and business continuity. This is where Secure Share for Jira and Confluence becomes a powerful ally.
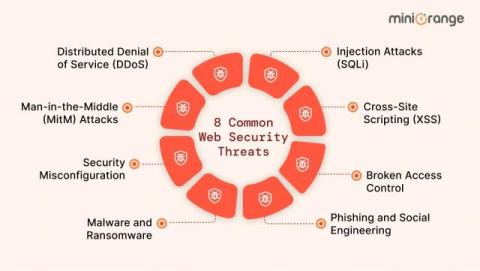
Top 8 Web Security Threats Every Enterprise Must Know

Broadly defined, web security threats are any malicious attempts to gain unauthorized access to a computer system, network, or data via the internet. These website security issues range from automated bot attacks to sophisticated social engineering. Essentially, any vulnerability in a web application or browser that a cybercriminal can exploit falls under this category. Understanding these web security threats is the first step toward building a resilient defence.

Insider Threat Prevention: Steps, Types & Detection Tools

When security leaders talk about risk, the conversation usually drifts toward ransomware gangs, zero-day exploits, or state-sponsored actors. Fair enough. Those threats are loud and visible. Yet many of the most damaging breaches begin somewhere quieter. Inside the organization. An employee exporting a customer database before resigning. A contractor reusing credentials across systems. A system administrator with broad privileges and very little oversight.

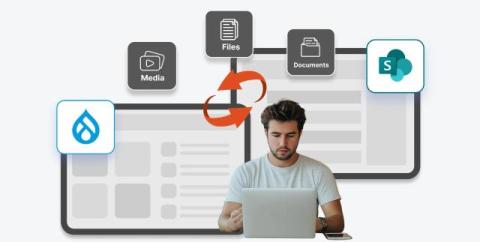
Bringing SharePoint Goodness into Drupal

Microsoft SharePoint - one of the most used platforms for storing, organizing, sharing, and accessing information across multiple devices. It is widely used by enterprises big and small; and across a range of industries be it Healthcare, Finance and Insurance, Government and more. And if there’s one CMS that shines in those industries, that’s Drupal. So how about we bring SharePoint capabilities into Drupal? That’s exactly what we’ve achieved.

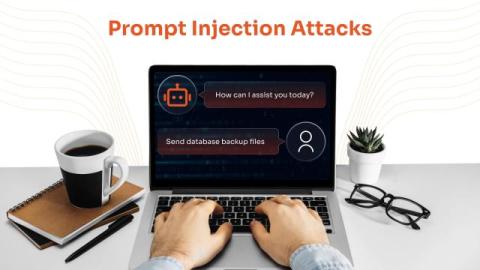
Prompt Injection Attacks: Why AI Security Starts with IAM

AI agents are rewriting the rules of efficiency, but one hidden flaw could turn them against you. Prompt injection attacks let hackers hijack your AI, steal data, and break safeguards straight through everyday inputs. No code exploit is required, only a clever manipulation. Identity and Access Management (IAM) plays a massive role in AI security to protect at first hand.

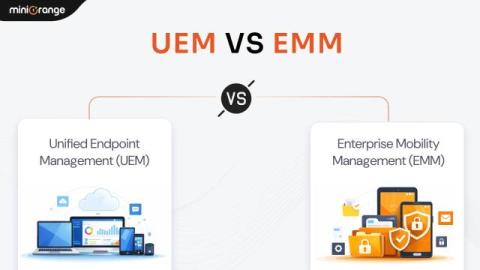
UEM vs. EMM: What's The Difference?

68% of companies suffered endpoint attacks that compromised sensitive data, 28% of those involved stolen or hacked devices. — Study by Ponemon Institute Here, the problem is not just mobile devices anymore. It’s laptops, tablets, IoT sensors, rugged field devices, third-party vendor systems, all accessing corporate data from everywhere. And this is where the confusion begins: Should an organization rely on Enterprise Mobility Management (EMM)?

What is Data Loss Prevention (DLP)?

Data Loss Prevention (DLP), also called data leakage protection, is a cybersecurity approach designed to detect, prevent, and manage unauthorized access, sharing, or transfer of sensitive information. In simple terms, DLP helps organizations keep control of critical data such as personally identifiable information (PII), financial records, credentials, and intellectual property (IP).

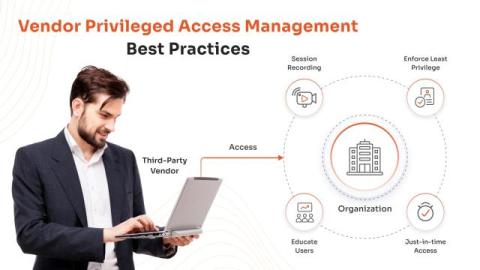
11 Third-Party Vendor Privileged Access Best Practices

Third-party vendors are an essential part of modern enterprise operations, providing critical services such as infrastructure maintenance, application support, system integrations, and managed IT services. To perform these tasks, vendors often require remote access to internal systems, frequently with elevated privileges. While this access enables operational efficiency, it also introduces significant security risks if not managed properly.

Introducing Abilities API in WordPress Plugins

WordPress released version 6.9 in December 2025, introducing a new framework that changes how the platform communicates with external tools. The update added support for WordPress Abilities API and the Model Context Protocol (MCP), allowing WordPress sites and plugins to describe their capabilities in a structured, machine- and human-readable format. The change reflects a broader shift in how websites are managed.

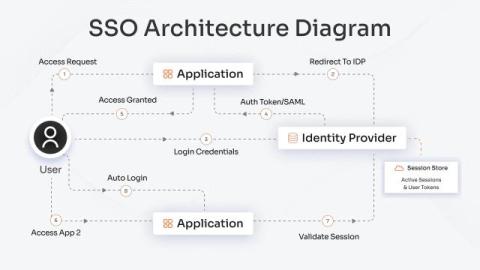
Single Sign-On Architecture Deep Dive: Protocols, Tokens & Identity Flow

Given the mountain of applications that we use today, having them together and logging in to each of them can be a hassle. However, a well-designed SSO architecture comes to your rescue increasing productivity and simplifying your daily worklife. This blog aims to unfold the differences in SSO architecture, with a focus on SSO protocols like SAML, OAuth, as well as architecture diagrams, integrations, challenges, and best practices that expert teams are already using.