Webinar: Infostealers in the Finance sector
Join us for a session dedicated to Infostealers in the financial sector.


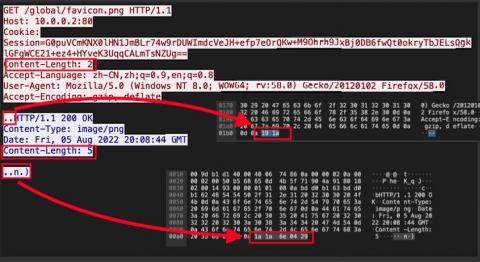
Security practitioners may know about common command-and-control (C2) frameworks, such as Cobalt Strike and Sliver, but fewer have likely heard of the so-called Chinese sibling framework “Manjusaka” (described by Talos in an excellent writeup). Like other C2 frameworks, we studied the Manjusaka implant/server network communications in our lab environment, and here we document some of the detection methods available. We have also open-sourced the content we describe.
The Mirai botnet is infamous for the impact and the everlasting effect it has had on the world. Since the inception and discovery of this malware in 2016, to present day and all the permutations that have spawned as a result, cybersecurity professionals have been keeping a keen eye on this form of Command and Control (C2 or CnC) malware and associated addresses.
Using the ChangeNTLM and SetNTLM commands in Mimikatz, attackers can manipulate user passwords and escalate their privileges in Active Directory. Let’s take a look at these commands and what they do.
2022 began with successful ransomware attacks against global IT and digital transformation providers, no thanks to the notorious LAPSUS$ ransomware gang. Often, any discussion about ransomware impact has mostly centered on affected organizations. Rightly so, as victimized organizations usually suffer significant disruption to their operations. In 2021, the US Federal Bureau of Investigation received 3,729 complaints identified as ransomware.
LockBit (a.k.a. ABCD) emerged in September 2019 and became one of the most relevant RaaS (Ransomware-as-a-Service) groups among others like REvil, BlackMatter, Night Sky, Maze, Conti and Netwalker. The group targets many organizations around the world with a double-extortion scheme, where the attackers steal sensitive data and threaten to leak everything if the ransom is not paid.
The NSO Group, the vendor behind Pegasus, is struggling financially, and to solve their money problems, the company is now considering selling their surveillanceware to governments with poor human rights records.
People have become the primary attack vector for cyber attackers around the world. As the Verizon Data Breach Investigations Report 2022 indicates, it is humans rather than technology that now represent the greatest risk to organizations. According to the SANS 2022 Security Awareness Report, the top three security risks that security professionals are concerned about are phishing, business email compromise (BEC) and ransomware, all closely related to human behavior.
The State of Ransomware in Government 2021 report finds that government agencies are facing a ransomware “national emergency.” Local governments in particular face higher rates of encryption during cyber attacks due to constrained budgets and organizational pressure to divert funds away from cybersecurity, leaving gaps in their data protection.