Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Priorities from the OpenSSF Secure Open Source Software Summit 2023

Snyk has been a long-time active participant in and sponsor of the Open Source Security Foundation (OpenSSF). We’re there because we believe in supporting its mission of securing the open source ecosystem. A recent summit meeting convened by the OpenSSF with the White House brought together various US Government departments for a chat about open source security.
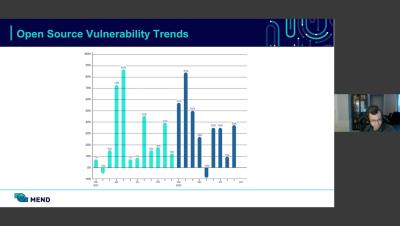
Securing the Software Supply Chain: Key Findings From the Mend Open Source Risk Report

Open source vulnerabilities are in permanent growth mode. A significant quarterly increase in the number of malicious packages published in registries such as npm and rubygems have shown the increasing need to protect against this trending attack. At the same time, companies struggle to close the remediation gap on known vulnerable open source code. It’s all in The Mend Open Source Risk Report, which details these and other significant risks posed by the ongoing rise in open source vulnerabilities and software supply chain attacks.

To OSINT and Beyond!

Open-Source Intelligence (OSINT) can be valuable for an organization and penetration testing engagements in several ways. Today, let me highlight two areas: Leaked Credentials and Files. As part of any security engagement, it is ideal, if not essential, that we look up our target’s leaked credentials and files, as many clients do not have a high level of visibility or awareness in this area.

Open Source CyberSecurity Tools for Hardening

Open-source cybersecurity tools offer a prime solution for independent security experts, emerging businesses, and even medium to large enterprises aiming to tailor their security framework. These tools serve as a foundational platform for fostering security advancements, integrating proprietary software code and security automation scripts.

Tips and Tools for Open Source Compliance

You don’t need us to tell you that open source software is becoming a very significant percentage of commercial software codebases. Open source components are free, stable, and enable you to focus your resources on the innovative and differentiated aspects of your work. But as the use of open source components increases, compliance with open source licenses has become a complex project of growing importance. So how can you stay on top of compliance and what tools are out there to help?

We're open-sourcing the library that powers 1Password's ability to log in with a passkey

You may have heard that 1Password beta testers can sign into websites using passkeys stored in their vaults. We’re actively developing the internal library powering passkey authentication, and now we’re open-sourcing it!

Open Cybersecurity Schema Framework (OCSF) Takes Flight with v1.0 Schema Release

It is not very often that we see cybersecurity vendors put aside competitive differences and ambitions to work towards a common goal that benefits the entire cybersecurity community. The Open Cybersecurity Schema Framework (OCSF) has shown to be an example of a productive industry-wide collaboration to facilitate a more secure environment for businesses, governments and individuals all over the globe.

Fireblocks' MPC-CMP code is Open-Source

In the pursuit of advancing security and transparency in the digital asset industry, Fireblocks has published our MPC-CMP code as open source under a limited license, along with the rest of our MPC library. As the demand for digital asset custody, tokenization, and Web3 among retail and financial institutions continues to rise, Fireblocks MPC-CMP has proven to be the most secure and reliable key management protocol.

Announcing the Open-Source Reliability Leaderboard: A New Resource for Preventive AppSec

We are excited to announce the inaugural edition of the Mend.io Open-Source Reliability Leaderboard! Powered by data from Renovate, the wildly popular open-source dependency management tool, the Leaderboard presents the top packages in terms of reliability across three of the most widely used languages.