Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

FedRAMP Penetration Testing Companies: Complete Buyer's Guide & Top Providers (2025)

With the arrival of cloud-conscious threat actors that are falling head over heels for LLM jacking and valid account abuse as cloud intrusions rose over 26% in 2024 vs 2023, being a Cloud Service Provider (CSP) you know that FedRAMP authorization is no longer about achieving a said compliance, you need to walk the extra mile to make sure you survive the ruthless competition in this space.
How a pentest strengthens audit evidence and adds value

Penetration testing and auditing are both methods of gaining assurance, but they operate from different angles. A pentest evaluates how well security controls stand up to real-world attack scenarios, while an audit examines whether those controls are designed, implemented, and maintained according to policy or recognised standards.

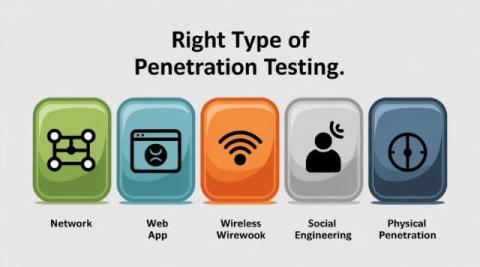
Ultimate guide to picking the right type of penetration testing

Securing your organization’s assets is more crucial than ever before! Penetration testing, also known as pen testing, has emerged as one of the best practices for identifying vulnerabilities before attackers do. This ultimate guide will help you understand how pen testing fits into an overall security strategy, outline key tools and methodologies, and detail how to ensure compliance with various regulatory frameworks.

How penetration testing services prove security and build client trust

In a world where data breaches continue to rise, organisations have become more discerning about who they trust with their information. It is no longer enough to claim that security is a priority — businesses must be able to prove it. Penetration testing, when conducted by qualified professionals, is one measure used as part of a comprehensive security strategy to provide that proof.

How to Get RBI Certification: A Pentesting Playbook for Banks, NBFCs, and Fintechs (Astra Security)

If vulnerabilities were a currency, they’d be inflating faster than anything else in the world. According to Astra’s State of Continuous Pentesting Report, 5.33 new ones are discovered every minute, i.e., by the time you’ve finished this paragraph, dozens more doors have swung open for attackers.

The Blueprint: How MSSPs Can Build a Profitable Pentest-as-a-Service (PtaaS) Offering

The latest 2025 Verizon Data Breach Investigations Report (DBIR) reveals a striking shift: exploitation of vulnerabilities has surged to become the initial access vector in approximately 20% of breaches, a 34% increase over the prior year. In an environment where cyber threats evolve faster than patch cycles, enterprises no longer view penetration testing as a checkbox exercise.

Why Pentesting Should Be on Every Startup's Launch Checklist

When launching a startup, every decision feels critical - from choosing your tech stack to hiring your first engineer. But in the rush to build fast and scale faster, one crucial element is too often left out of the launch checklist: penetration testing. For early-stage companies, the idea of investing in a pentesting tool can feel like a "later" priority - something reserved for larger enterprises with established revenue and complex infrastructure. But the truth is, security debt accumulates from day one, and the longer it's ignored, the more expensive it becomes.

Threat-Led Penetration Testing by Astra Security

Basic security audits won’t stop ransomware criminals who move faster than most teams can deploy patches, especially now, as supply chain attacks leverage trusted partners, and advanced persistent threats (APTs) hide undetected in networks for months. Fifty-two percent of organizations worldwide report at least one supply chain partner targeted by ransomware, putting their own networks dangerously at risk.

Two Tools, One Strategy: Pairing Vulnerability Scanning and Pen Testing for Maximum Protection

Penetration Testing and Managed Vulnerability Scanning (MVS) are often mentioned in the same breath, yet their true value emerges when they are combined. Each plays a distinct role in building a strong Offensive Security program, and together they form a powerful foundation for reducing risk and improving resilience. However, it is common for those not fully immersed in cybersecurity practices to either confuse or conflate these two practices.