Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Detection and Investigation Using Devo: REvil Ransomware Kaseya VSA

On July 3, 2021, Kaseya reported1 a potential attack against its Virtual System/Server Administrator (VSA) that apparently had been limited to a small number of on-premises customers. Kaseya recommended an immediate shutdown of the VSA server until further notice. The small number of affected customers grew to thousands in just a few hours.
Sumo Logic Named a Visionary in the 2021 Gartner Magic Quadrant for SIEM for the First Time

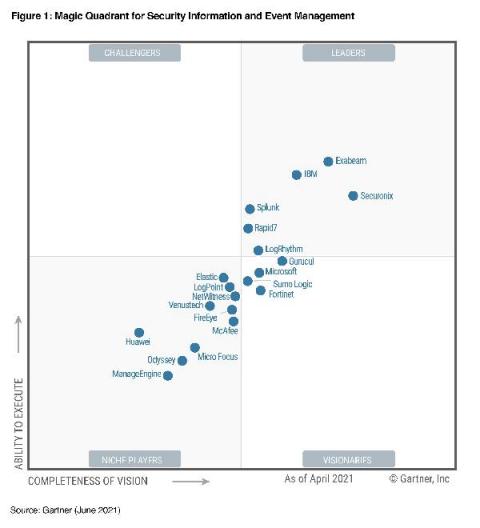
The Sumo Logic team is excited to announce that it has been named a Visionary in the Gartner 2021 Magic Quadrant for Security Information Event Management (SIEM). We believe our placement in the Visionary quadrant reflects the value and success our customers have realized by using our cloud-native security platform and the innovative ways in which it solves SIEM and modern security operations use cases.

Elastic Security Recognized in the 2021 Gartner Magic Quadrant for SIEM

We’re excited to share that Elastic Security has been recognized in the 2021 Gartner Magic Quadrant for Security Information and Event Management (SIEM). Elastic Security is the latest Elastic solution to be recognized in a 2021 Gartner Magic Quadrant report, following the 2021 Magic Quadrant for Insight Engines and 2021 Magic Quadrant for Application Performance Monitoring.

Splunk Named a Leader in the 2021 Gartner SIEM Magic Quadrant for the Eighth Time

Splunk was named a Leader for the eighth consecutive time this week in the Gartner Magic Quadrant for Security Information and Event Management (SIEM)*. In our opinion, this recognition marks one of the longest running recognitions in the history of the SIEM market. The recognition comes on the heels of Splunk also being ranked No.

Splunk Named Market Share Leader in ITOM and SIEM Reports

2020 was a challenging year for modern enterprises. In under a year, we experienced a decade's worth of transformation while a global pandemic raged on. And while the worst of COVID-19 will hopefully soon be behind us, the need to continuously transform our digital environment is unequivocally here to stay. We've already seen an example of this, thanks to a significant increase in data generated from across the business.

EventSentry on GitHub: PowerShell module, templates and more!

Since we’ve accumulated a lot of resources around EventSentry that are updated frequently, we’ve decided to launch a GitHub page where anyone can access and download scripts, configuration templates, screen backgrounds and our brand-new PowerShell module that is still under development.

Is All Data Security Data?

There’s an old expression: When you’re a hammer, everything looks like a nail. Therefore, is it right for a security company such as Devo to consider all data security data? Let’s examine that concept. Recently I participated in a panel discussion at the GDS Security Insight Summit Europe with my colleague Dean Robertson who heads solution engineering for Devo in EMEA.

Threat Hunting with Cloud SIEM

Threat hunting is emerging as a must-have addition to cybersecurity strategies. By enabling organizations to find and mitigate threats before they ever touch their networks or systems, threat hunting provides the basis for a more proactive security posture – and one that delivers higher ROI on security tools and processes. How can businesses actually add threat hunting to their security arsenals? That’s where solutions like Sumo Logic's Cloud SIEM come in.