Zenity Labs is publicly launching AI Total: a free service that runs an AI agent skill in a sandbox and tells you what it actually did, before you let it near your agents.
When a vendor’s risk score changes, a TPRM team can see what issues were flagged, why they matter, and what remediation steps are recommended next. But improving a vendor’s risk posture is not always as simple as working through each risk finding one by one. Sometimes the bigger pattern sits at the asset level.
Cybersecurity Awareness Month has encouraged safer online behaviour every October since 2004, but AI-enabled attacks are changing what awareness needs to look like. This article looks at the campaign's history, the latest UK threat data, and why organisations should ground their awareness efforts in real threat intelligence.
Most AD cleanup processes stop at the domain boundary, but hybrid audits don’t. Here’s what auditors actually check across Active Directory and Entra ID, and the gaps that trip up teams in their first review. Ask a few IT teams how they handle offboarding and you’ll hear the same answer: disable the account in Active Directory, close the ticket, and move on.
Separation of duties, also called segregation of duties, is a control that splits a sensitive business process across more than one person so no single user can both execute and approve the same action. Organizations enforce it by mapping conflicting duties into a matrix, applying role-based access control and least privilege, requiring independent approval on high-risk transactions, and reviewing access on a set cadence.
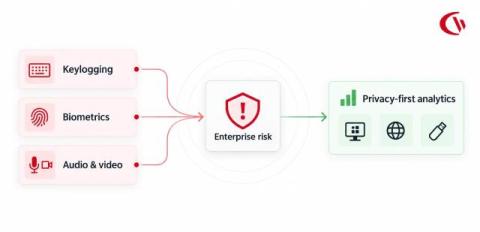
For years, employers assumed that owning the laptop and the network meant unlimited monitoring rights. In 2026, that assumption no longer holds. Federal wiretap law, state biometric statutes, all-party consent requirements and the EU Artificial Intelligence Act each limit what an employer can collect and how. Most workplace surveillance software must weigh the competing goals of safeguarding corporate resources and respecting employees’ right to privacy.
Transitional relief normally works one way. A new rule arrives, existing products are carved out or given years, and anything built afterwards complies from the start. The marking obligation for synthetic content inverts that. Article 50 has applied since 2 August 2026, and a targeted transitional period gives extra time to systems that were already on the market rather than to new ones.
A trained model is expensive to produce, cheap to copy and impossible to recall. Where one is taken, the organization still holds it, and the loss is not that the asset is gone. What ends is exclusivity. Lost exclusivity is a different quantity from a destroyed asset, it carries no notification obligation, it appears in no breach cost dataset, and most estimates therefore put it at zero by omission rather than by judgment.
You start the day with reports that your employees cannot access critical systems. A ransom note soon explains why: attackers have encrypted them and demand $2 million in bitcoin for a decryption key. Your team contains the attack and confirms that the backups are safe, yet this is only the beginning. Restoring your servers can take weeks, but recovering the business can take much longer.
A lot of the current conversation about agentic SOCs is about triage. Faster detection, faster investigation, alerts resolved in minutes instead of hours. When we set out to build the Aurora Agentic SOC, we didn’t just want to make triage faster. We fundamentally re-engineered our SOC to strengthen every job it does, and enhancing the Concierge Experience for our customers was a key part of that.