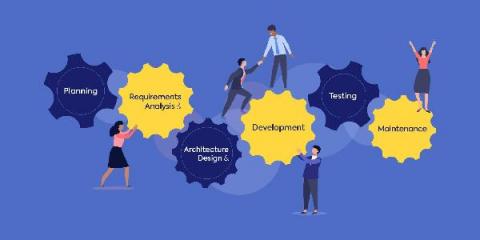
The adoption of agile practices has resulted in the emergence of shift-lift testing, where testing is performed much earlier in the Software Development LifeCycle (SDLC). Traditional waterfall models performed testing to the right of, or following, development. The benefits of testing earlier and more often cannot be underestimated. However, where does this leave security and security testing?
Continuing on the successful webinar journey, last week Appknox hosted a webinar on "Secure Coding Practices to Prevent Vulnerabilities in SDLC." Focusing on secure coding best practices, our experts busted several myths and misconceptions regarding mobile app security in the webinar and highlighted several client-side misconfigurations which generally go unnoticed by the app developers.
The ever-evolving threat landscape in our software development ecosystem demands that we put some thought into the security controls that we use throughout development and delivery in order to keep the bad guys away. This is where the secure software development life cycle (SSDLC) comes into play. Organizations need to make sure that beyond providing their customers with innovative products ahead of the competition, their security is on point every step of the way throughout the SDLC.
The SolarWinds hack, which has affected high-profile Fortune 500 companies and large U.S. federal government agencies, has put the spotlight on software development security — a critical issue for the DevOps community and for JFrog. At a fundamental level, if the code released via CI/CD pipelines is unsafe, all other DevOps benefits are for naught.
The PCI Security Standards Council (SSC) is a global organization that aims to protect payment transactions and consumer data by developing standards and services for payment software vendors that drive education, awareness, and implementation. Since payment software is constantly changing, the SSC is constantly evolving and adapting its standards to ensure that vulnerabilities and cyberattacks are minimized.
At Outpost24, we’re committed to providing information security testing solutions to not only fit seamlessly into the SDLC, but also to enhance our customers’ experiences in implementing and maintaining their best practices to ensure their SDLC leads to a strong security posture and comprehensive resiliency around their full stack.