Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Top 10 Automated Access Control Systems

Manual access requests and long-lived credentials pose a significant scaling challenge for engineering teams, even as they automate pipelines, testing, delivery, and monitoring. As the volume of machine identities grows, the sheer volume of permissions makes manual review and revocation unmanageable, increasing risks of stale tokens and silent privilege exposure. Nearly 47% of cloud intrusions stem from weak or mismanaged credentials, according to a Google Cloud report.
The future of AI in Identity Security, with Martin Kuppinger and One Identity CEO Praerit Garg

Join One Identity CEO Praerit Garg and KuppingerCole Founder and Principal Analyst Martin Kuppinger as they discuss the evolution of IAM and thefuture of AI in Identity Security.

Secret Management: A Step-by-step Guide to NHI Security

It’s not hard for secrets to sprawl, buried under layers of commits and forgotten branches. Most teams don’t notice it until one bad push exposes everything. Secret leaks don’t come from breaches, but from configuration drift and forgotten credentials; a gap that traditional vault tools struggle to close on their own. Here’s the scale of that mess. Machine identities now outnumber human users by more than 80 to 1, and each one relies on credentials to function.

Better Together: Apono and 1Password Join Forces to Deliver Secure, Just-in-Time Access to Secrets

We’re excited to announce Apono integration with 1Password to help organizations control, automate, and audit access to sensitive credentials and secrets bringing stronger security and smoother operations to teams everywhere. This new integration enables customers to enforce Zero Standing Privileges (ZSP) and provision Just-in-Time (JIT) and just-enough access (JEA) to secrets stored in 1Password Enterprise Password Manager through Apono’s automated access flows.

AI Model Poisoning, Uneven Regulation, and the New Battle for Digital Trust: Top Predictions for 2026 Revealed

The next wave of supply-chain breaches go beyond exploiting software dependencies and weaponize the trust layer between organizations and their vendors/partners. Off-the-shelf toolkits, some of them state-sponsored, are lowering the barrier to entry for third-party compromises. As a result, regulators are hard-coding “continuous verification” into frameworks such as NIS2, DORA, and the EU Cyber Resilience Act.

Introducing Spaces Management: Safe, Scalable Access Governance for Large Engineering Organizations

Large engineering organizations all run into the same challenge: as teams grow, clouds multiply, and environments diversify, access governance becomes noisy, risky, and difficult to delegate safely. Apono’s new Spaces Management feature gives enterprises a clean, scalable way to segment access governance across departments without spinning up multiple tenants or losing centralized control.

Privileged Entitlements Management (PEM): A Complete Guide

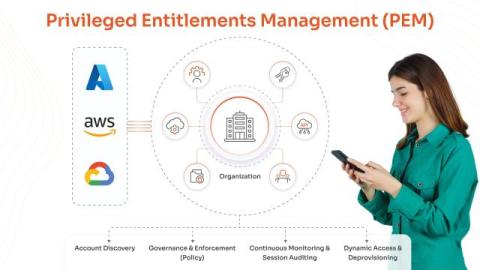
Privileged Entitlements Management (PEM) is a specialized cybersecurity practice that focuses on securely managing high-risk entitlements, also known as permissions, access rights, or privileges, which grant access to sensitive data, critical resources, and essential services across an organization's IT infrastructure.

How Contractor Privileged Access Failures Exposed Data Across 45 Federal Agencies

Earlier this year, twin brothers Muneeb and Sohaib Akhter, both government contractors, were fired from their employer. Minutes later, they began a weeklong insider attack that compromised or destroyed data belonging to more than 45 federal agencies.

Top 12 Privileged Access Management (PAM) Use Cases in 2026

Privileged Access Management (PAM) is your organization's security control center for managing and monitoring high-level access to critical systems. Think of it as a sophisticated vault system that safeguards your most powerful administrative credentials while maintaining detailed audit trails of their usage. As we head into 2026, PAM has become crucial. Here's why: Cyberattacks are getting scarier and more complicated.

7 Tips for Just-in-Time Privileged Access Management You Need to Implement Today

Managing access can become tedious and clunky. Someone always ends up with too much power, someone else is locked out when something’s on fire, and no one remembers who approved what in the first place. It’s the slow creep of “we’ll fix it later.” However, that “later” is catching up.