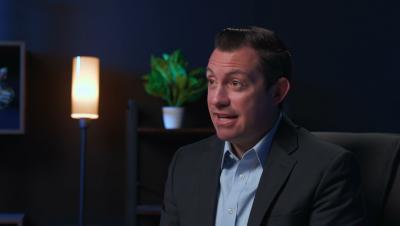
Adam Marrè, Chief Information Security Officer at Arctic Wolf, discusses a devastating phishing attack and why it's vital to conduct a personal analysis of what you're presenting to the world through social media.
As the Chief Information Security Officer (CISO) at Arctic Wolf, I have a deep bench of security experts I can leverage to provide the organization with robust risk management, threat detection, security awareness training, and incident response. That’s an advantage that small businesses often don’t have.
The cyber insurance market has matured rapidly over the past two years in the face of ever-evolving risk. Factors such as increased ransomware activity, ballooned claims frequency and loss severity, coupled with soaring market demand have brought us to what is referred to as the “second wave” of cyber insurance — a revolution in the way businesses are evaluated, underwritten and protected.
Arctic Wolf’s The State of Cybersecurity: 2023 Trends report revealed a painful, yet unsurprising statistic: 68% of organizations identified staffing-related issues as their number one threat to achieving their security objectives. Breaking that down further, 32% of organizations are having difficulty with hiring and retaining staff. The remaining 36% feel their existing security team lacks the necessary expertise.
On June 23, 2023, Fortinet disclosed a critical Remote Code Execution (RCE) vulnerability (CVE-2023-33299) affecting FortiNAC, a network access control solution utilized by organizations to manage network access policies and compliance. This vulnerability is the result of the deserialization of untrusted data. Deserialization vulnerabilities such as this one are dangerous because a threat actor can insert a modified serialized object into the system which leads to unauthenticated RCE.
If you think it isn't possible for cyber criminals to compromise multi-factor authentication, think again. Learn about SIM swapping, including how it works, why it's successful, and tips on how to protect your accounts.
Social engineers are looking for all the information they can use against you or your organization, meaning documents and devices must be disposed of properly. Find out more in Cipher's latest mission, where we see him attempt to stop a nefarious cyber gang in their tracks.
Strong, resilient security operations require the proper melding of people, technology, and processes to achieve the goal of reducing the likelihood and impact of cyber threats. The right security operations center (SOC) will strengthen the overall security resiliency of an organization. The wrong one will tax your team — leading to mistakes, breaches, and losses.
Nobody can win without the support of their team. Hélio Castroneves & Simon Pagenaud of the Meyer Shank Racing team discuss the importance of Security Awareness for organizations, and how Arctic Wolf prepares your employees to recognize and neutralize social engineering attacks and human error—helping to end cyber risk at your organization.
On June 9th 2023, security researchers from Olympe CyberDefense published a blog stating that they responsibly disclosed a critical vulnerability in SSL-VPN firewalls to Fortinet. This vulnerability, CVE-2023-27997, is a critical, pre-authentication RCE vulnerability that impacts all versions of Fortinet SSL-VPN firewalls, even if multi-factor authentication (MFA) is enabled. The security researchers responsibly disclosed the vulnerability to Fortinet.